VULNERABILITY INTELLIGENCE
CVE-2026-8256
CVSS score2.4 LOW
EPSS probability0.20%
CISA KEVNot currently listed
Published2026-05-11
Last modified2026-07-24
CVSS vectorCVSS:3.1/AV:N/AC:L/PR:H/UI:R/S:U/C:N/I:L/A:N
Description
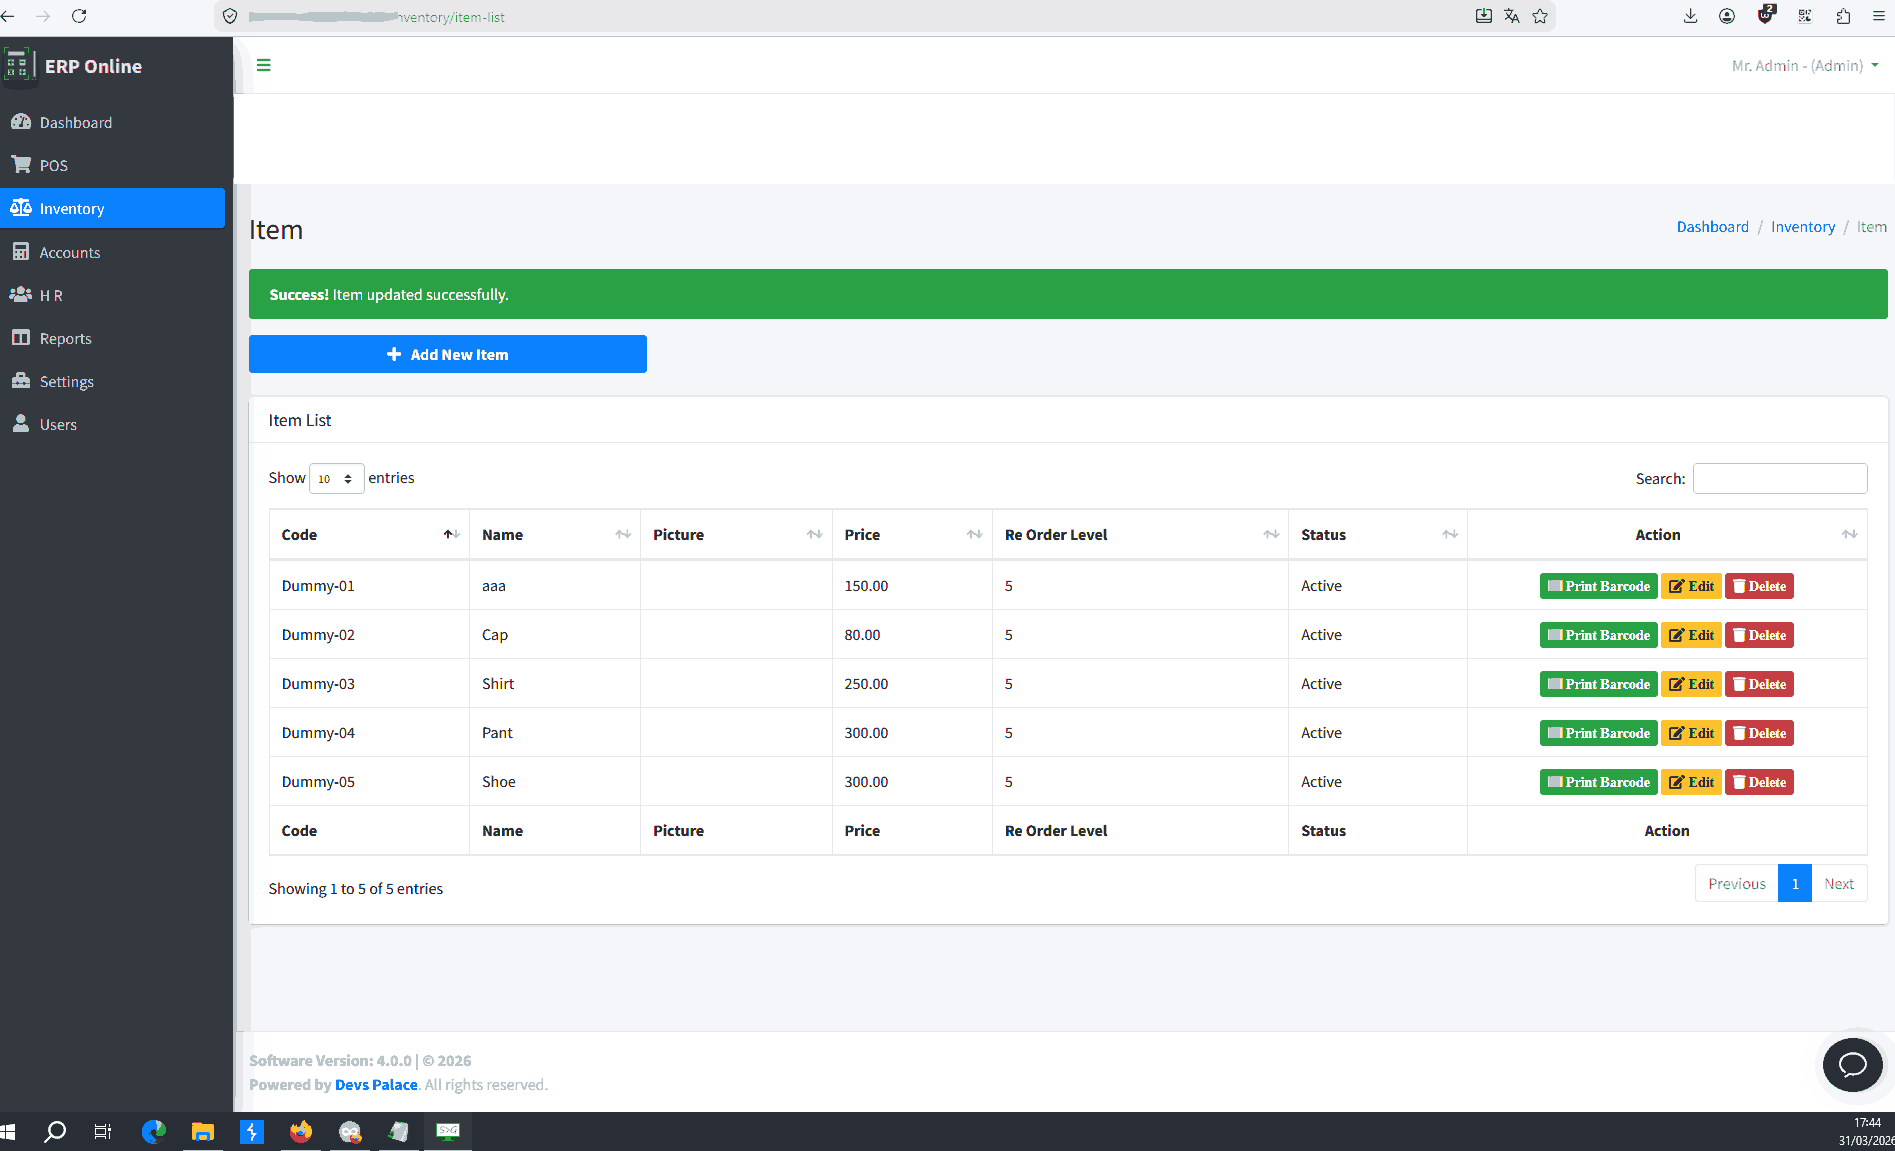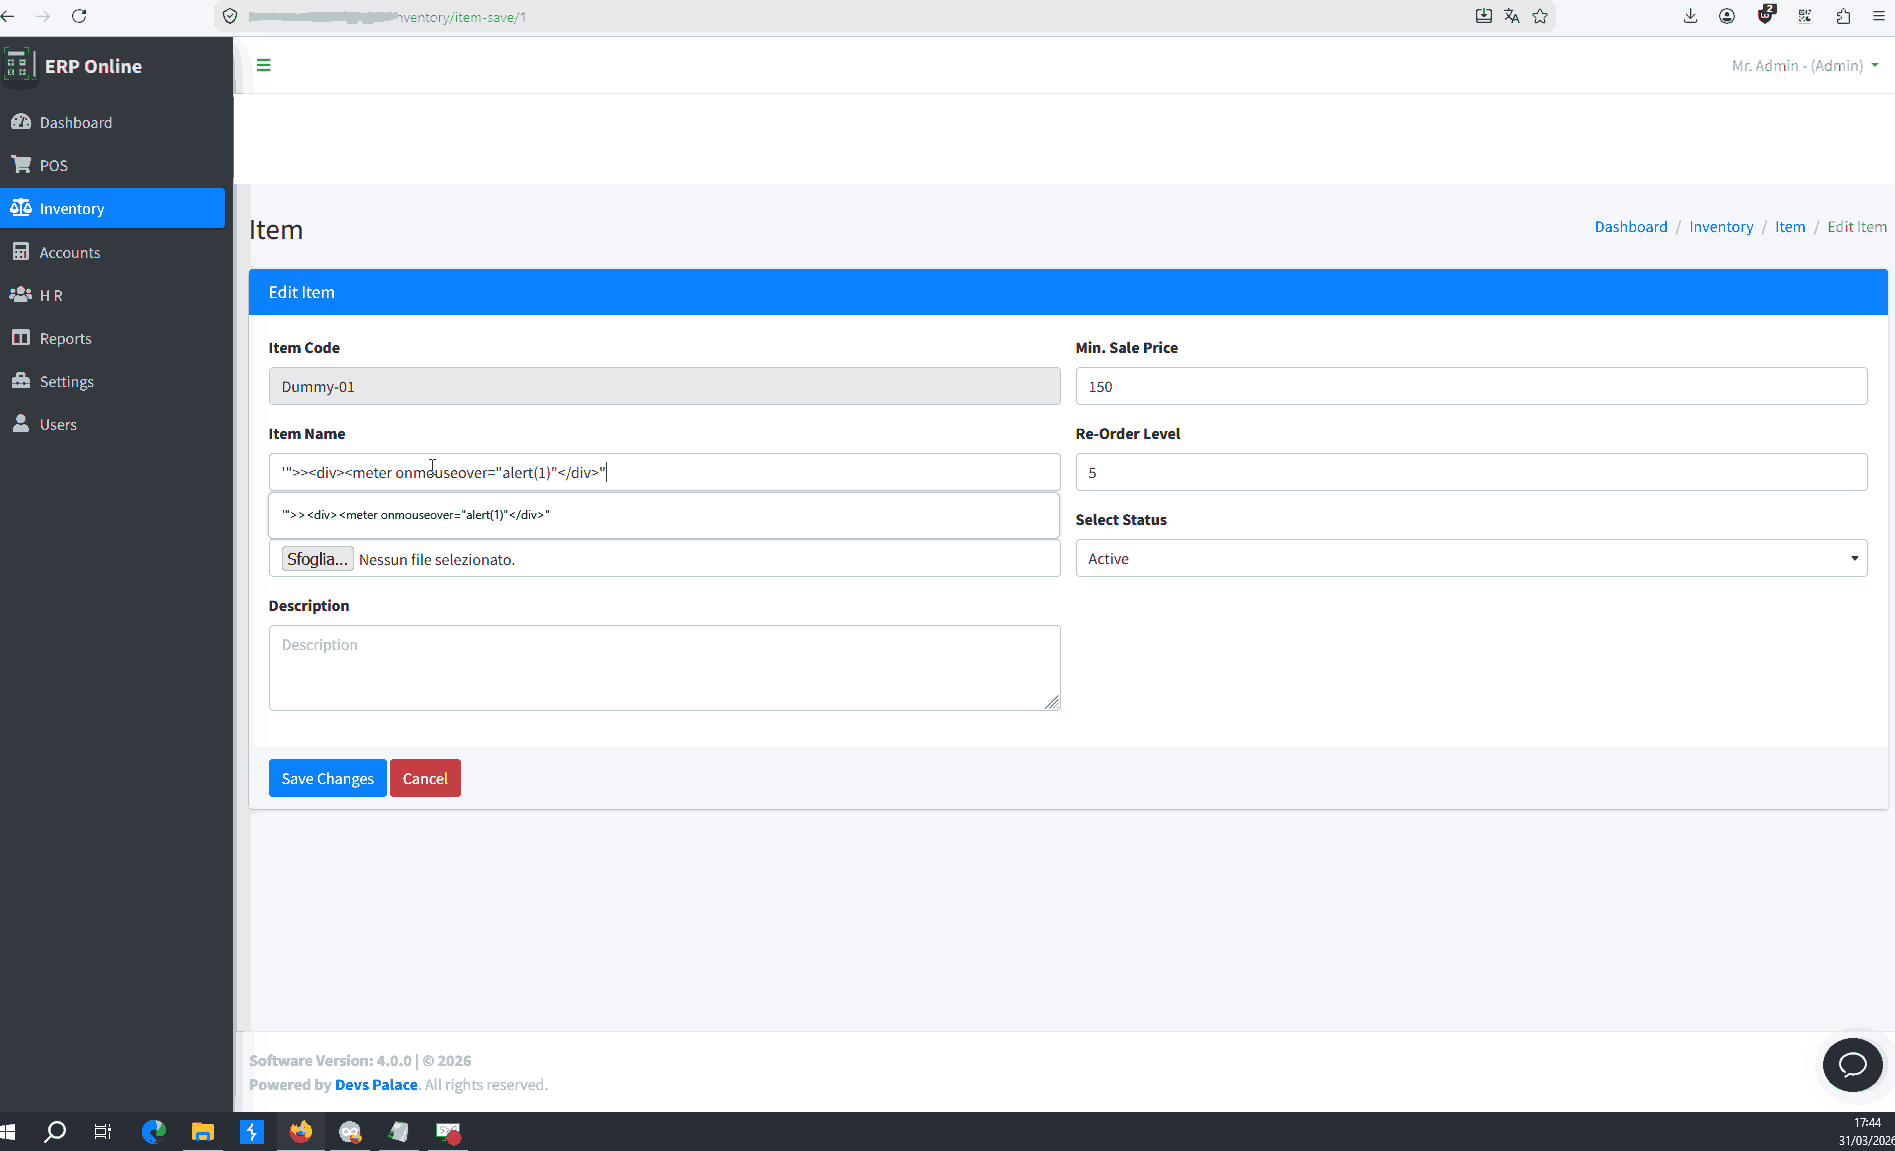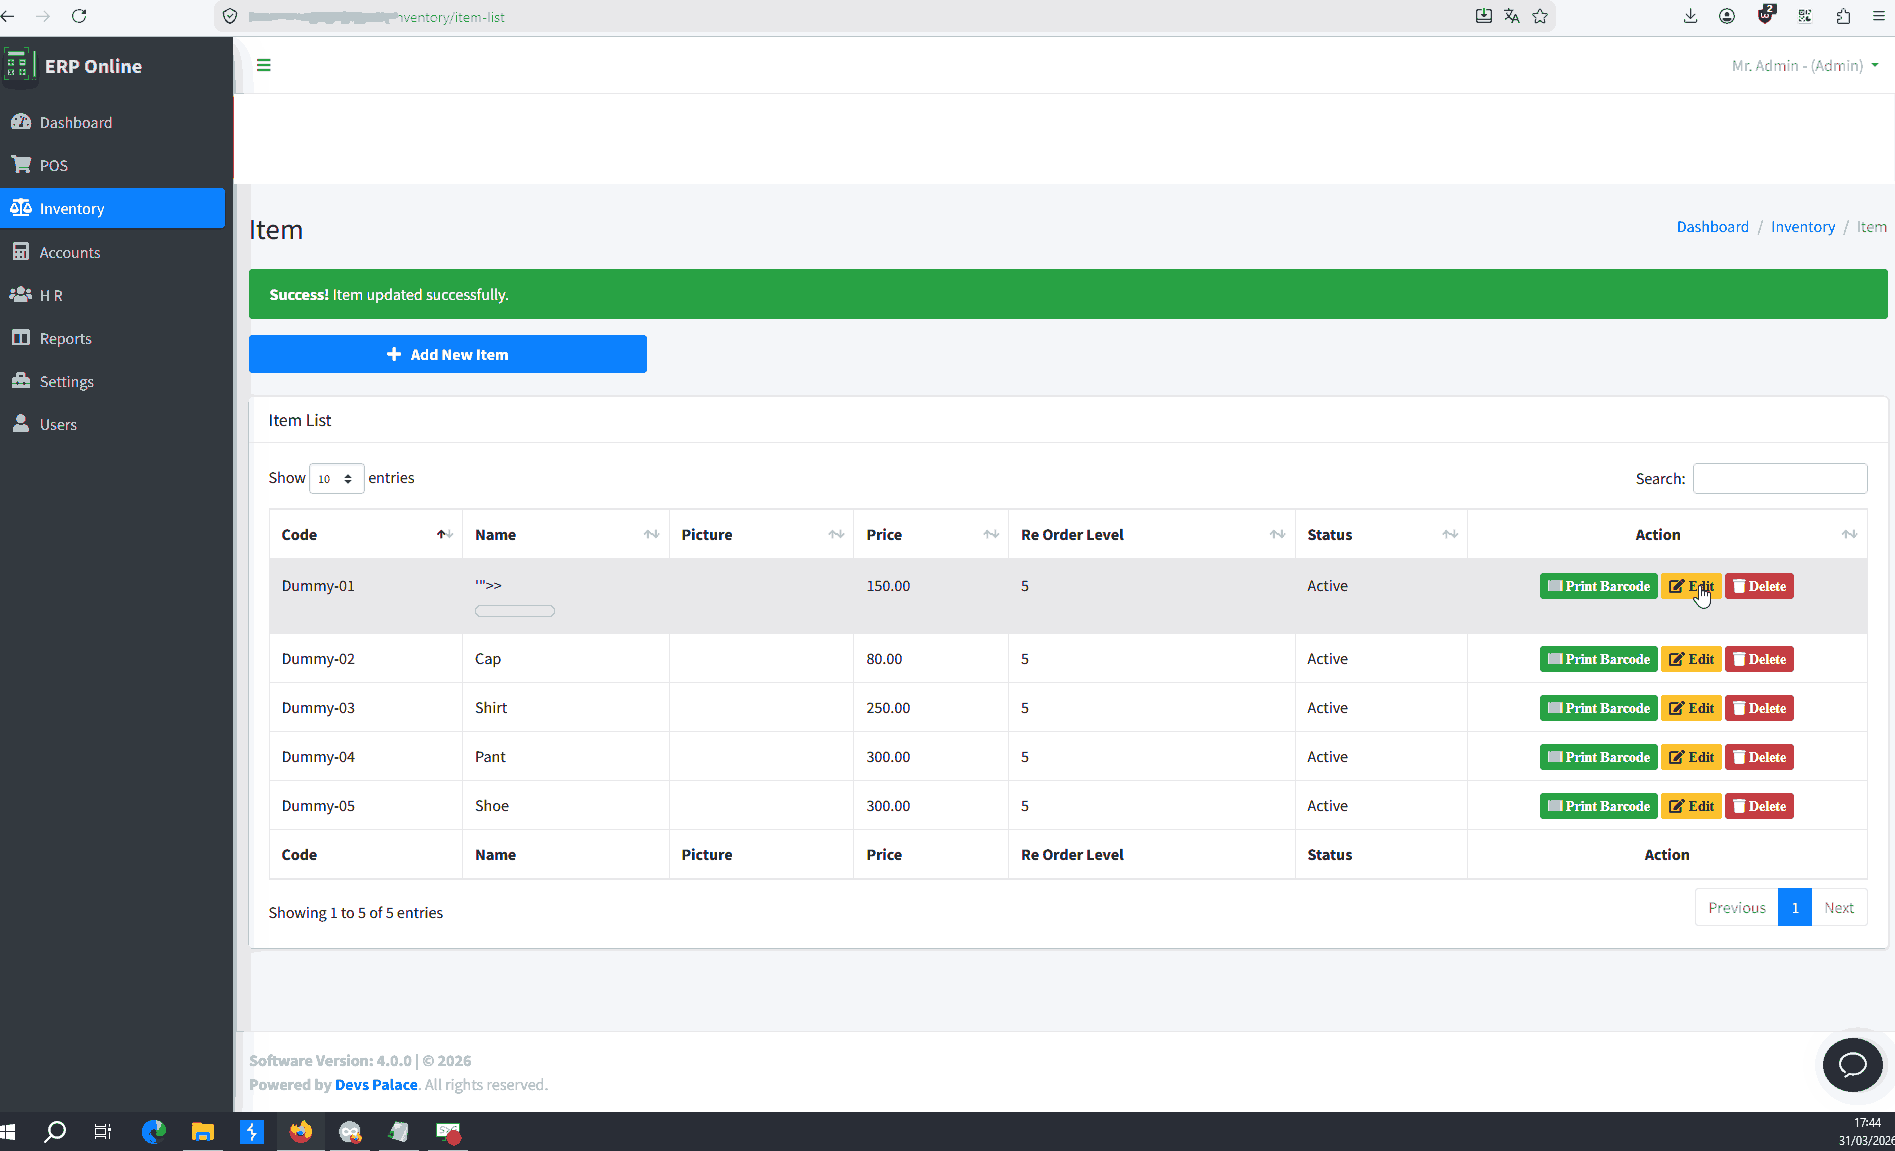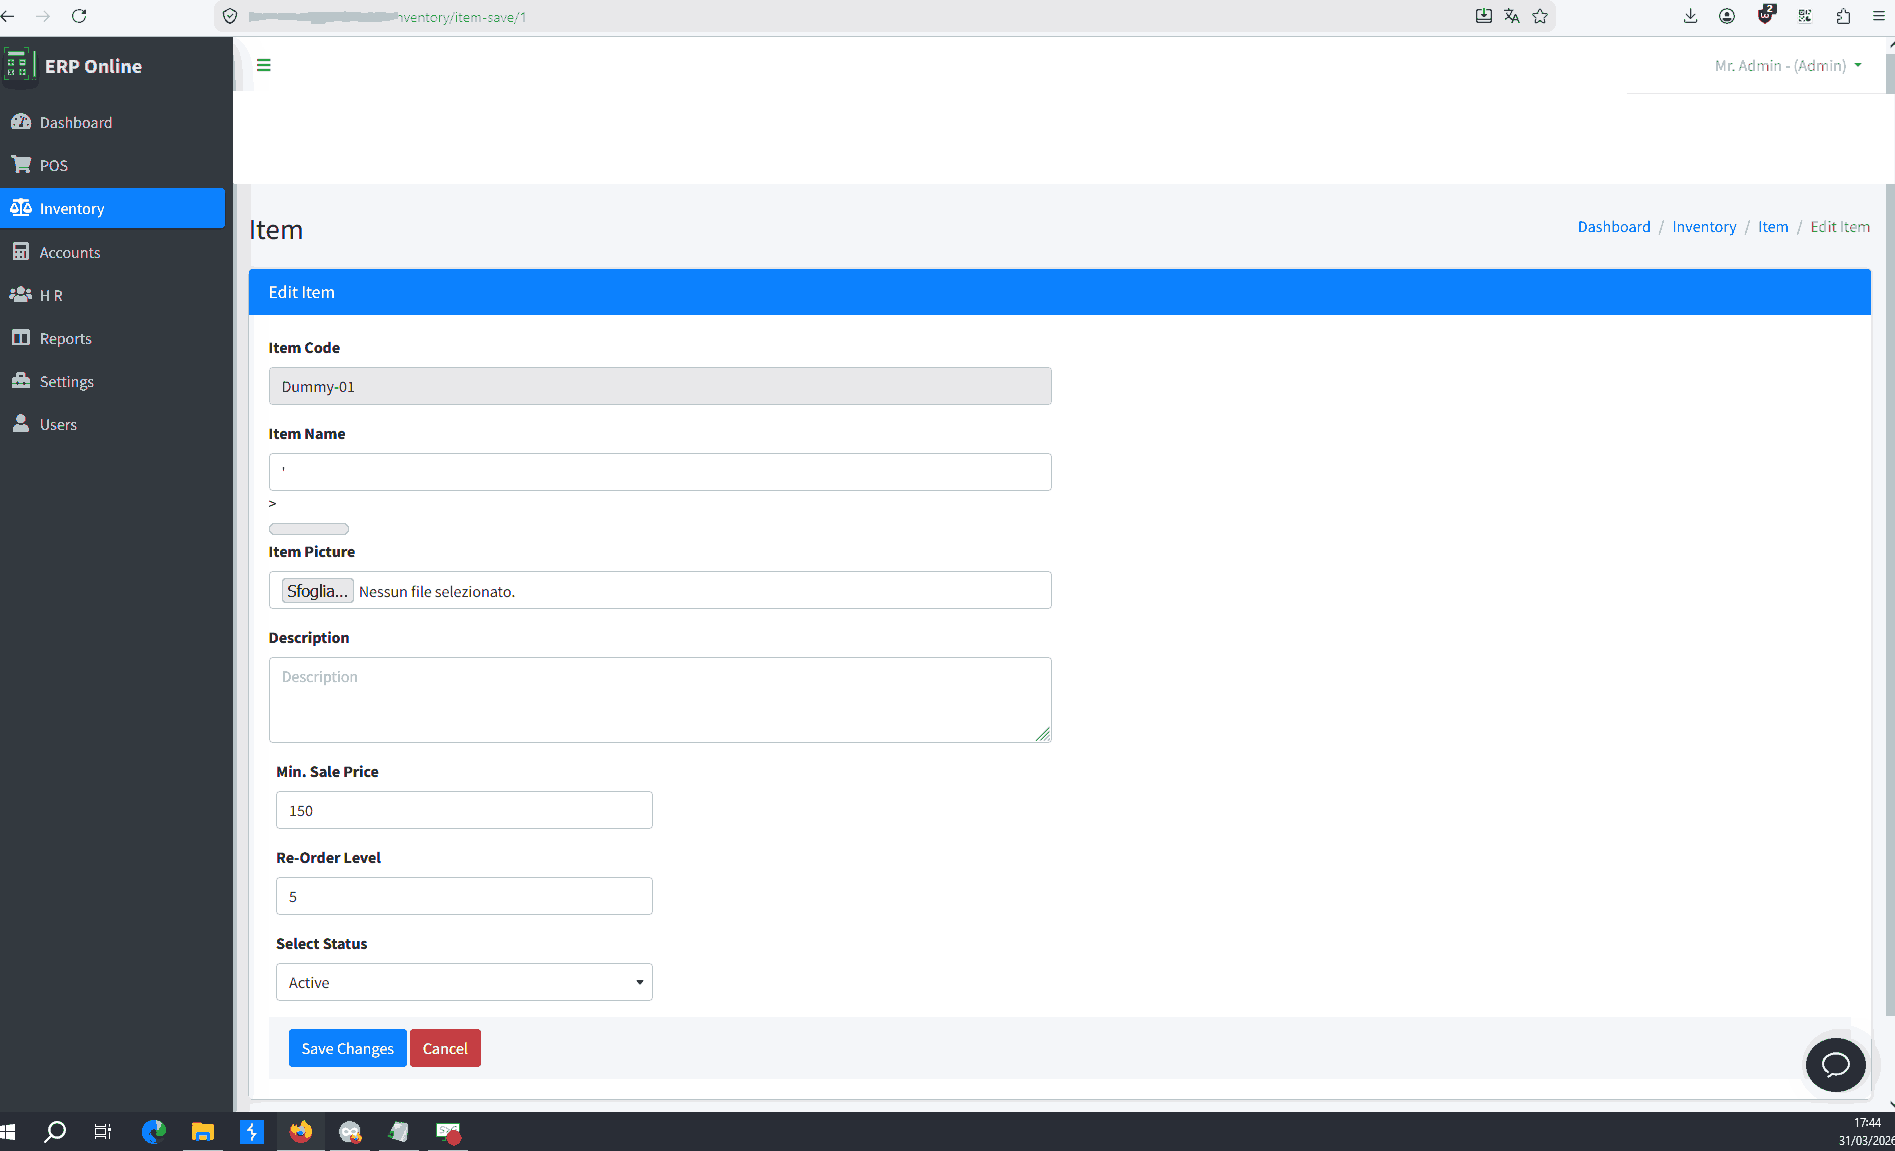
A security vulnerability has been detected in Devs Palace ERP Online up to 4.0.0. This vulnerability affects unknown code of the file /accounts/mr-save. Such manipulation leads to cross site scripting. The attack can be launched remotely. The exploit has been disclosed publicly and may be used. The vendor was contacted early about this disclosure but did not respond in any way.
Weakness classification
- cna@vuldb.com: CWE-79