VULNERABILITY INTELLIGENCE
CVE-2026-6743
CVSS score5.1 MEDIUM
EPSS probability0.19%
CISA KEVNot currently listed
Published2026-04-21
Last modified2026-10-26
CVSS vectorCVSS:4.0/AV:N/AC:L/AT:N/PR:L/UI:P/VC:N/VI:L/VA:N/SC:N/SI:N/SA:N/E:P/CR:X/IR:X/AR:X/MAV:X/MAC:X/MAT:X/MPR:X/MUI:X/MVC:X/MVI:X/MVA:X/MSC:X/MSI:X/MSA:X/S:X/AU:X/R:X/V:X/RE:X/U:X
Description
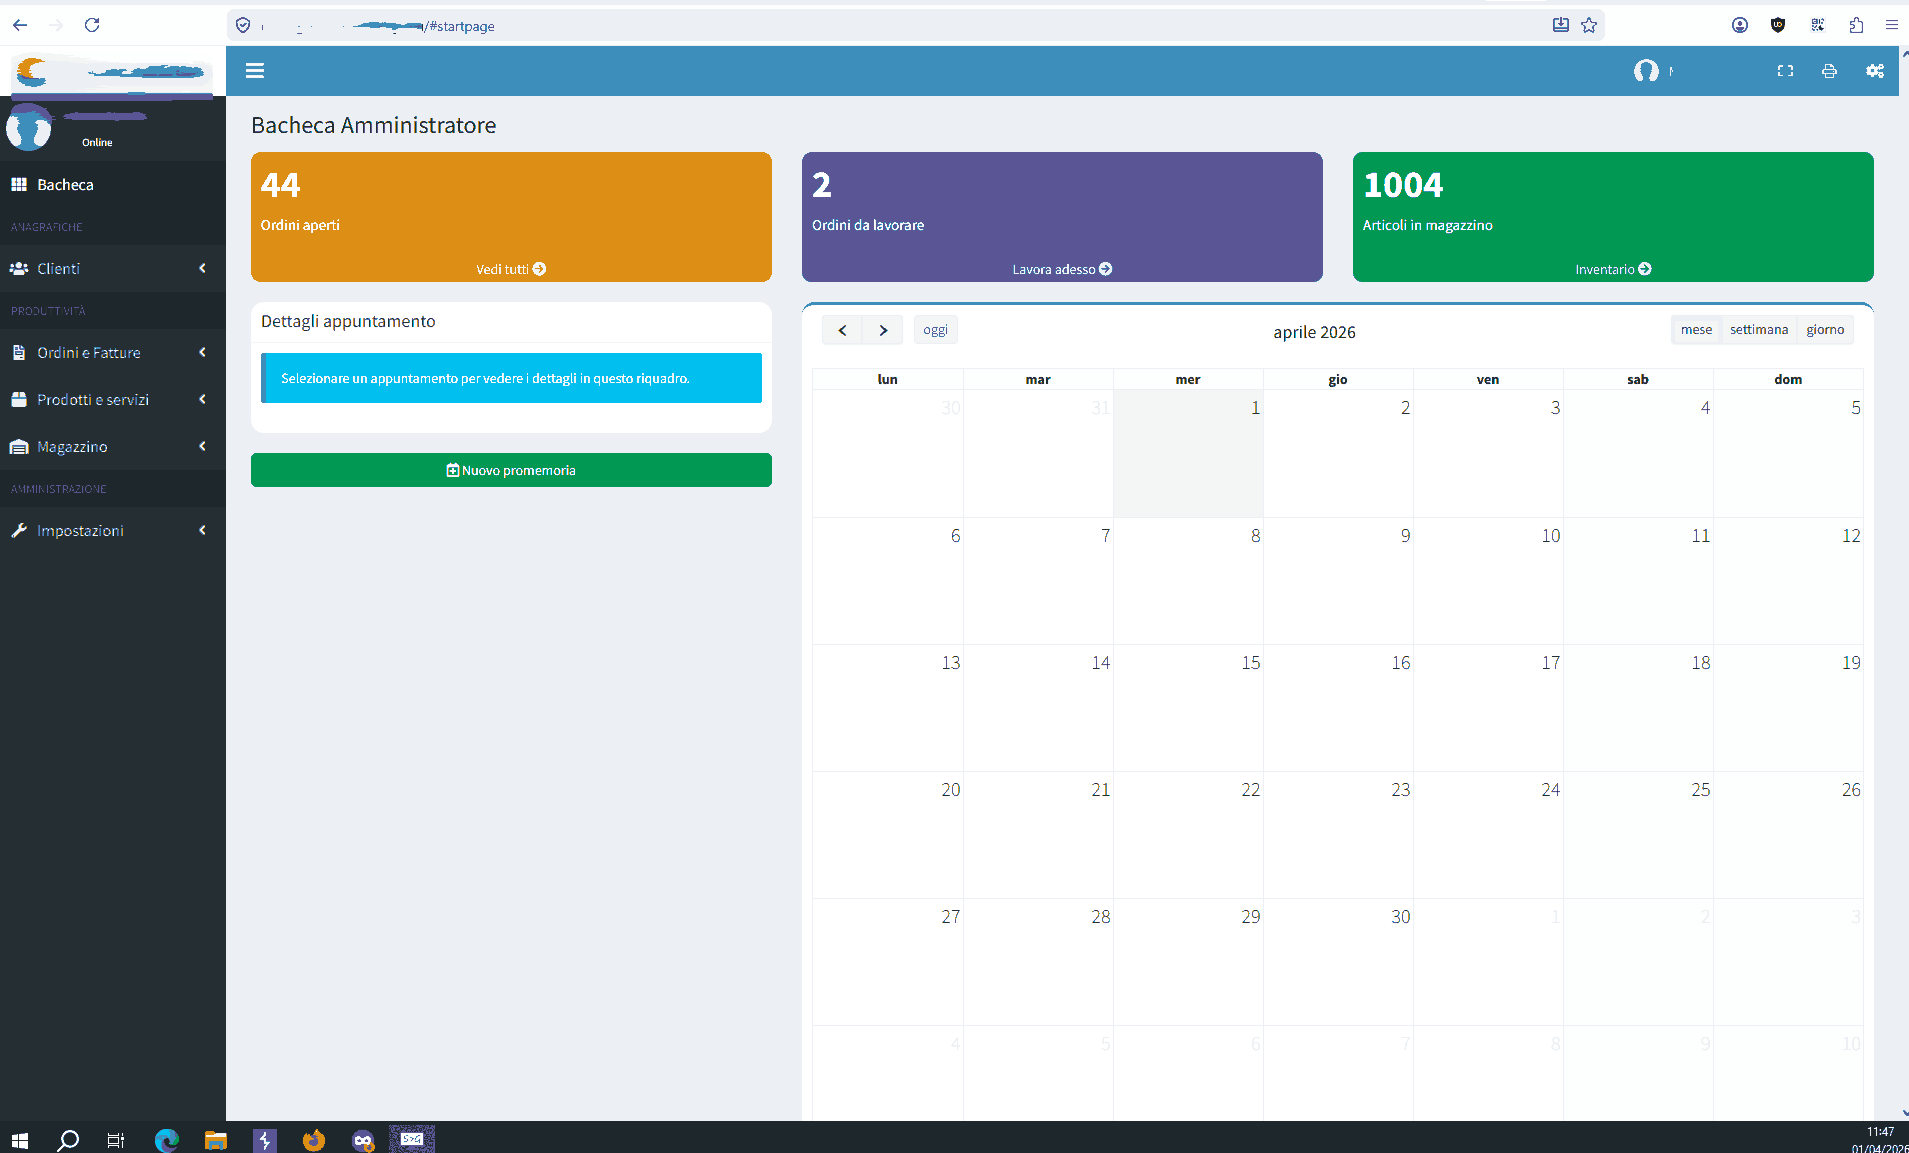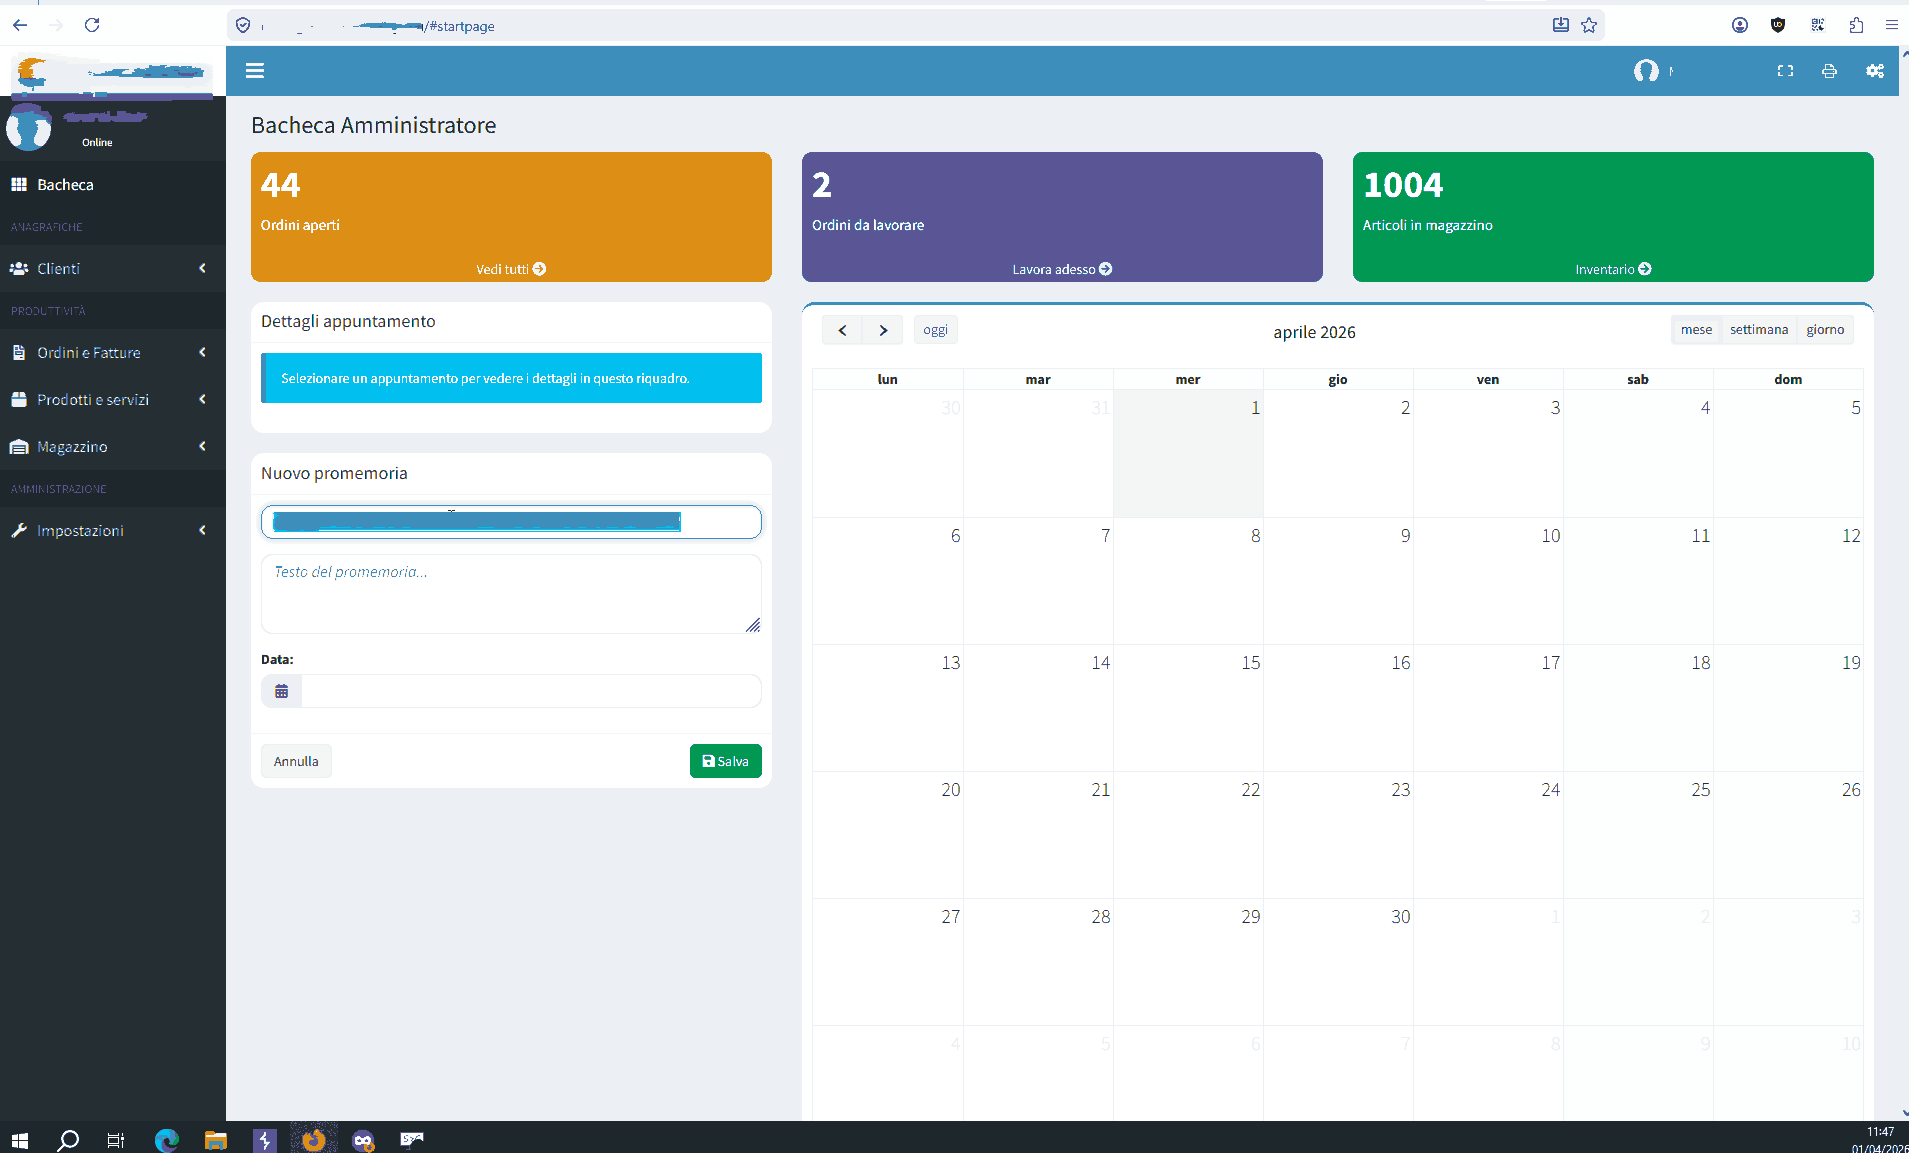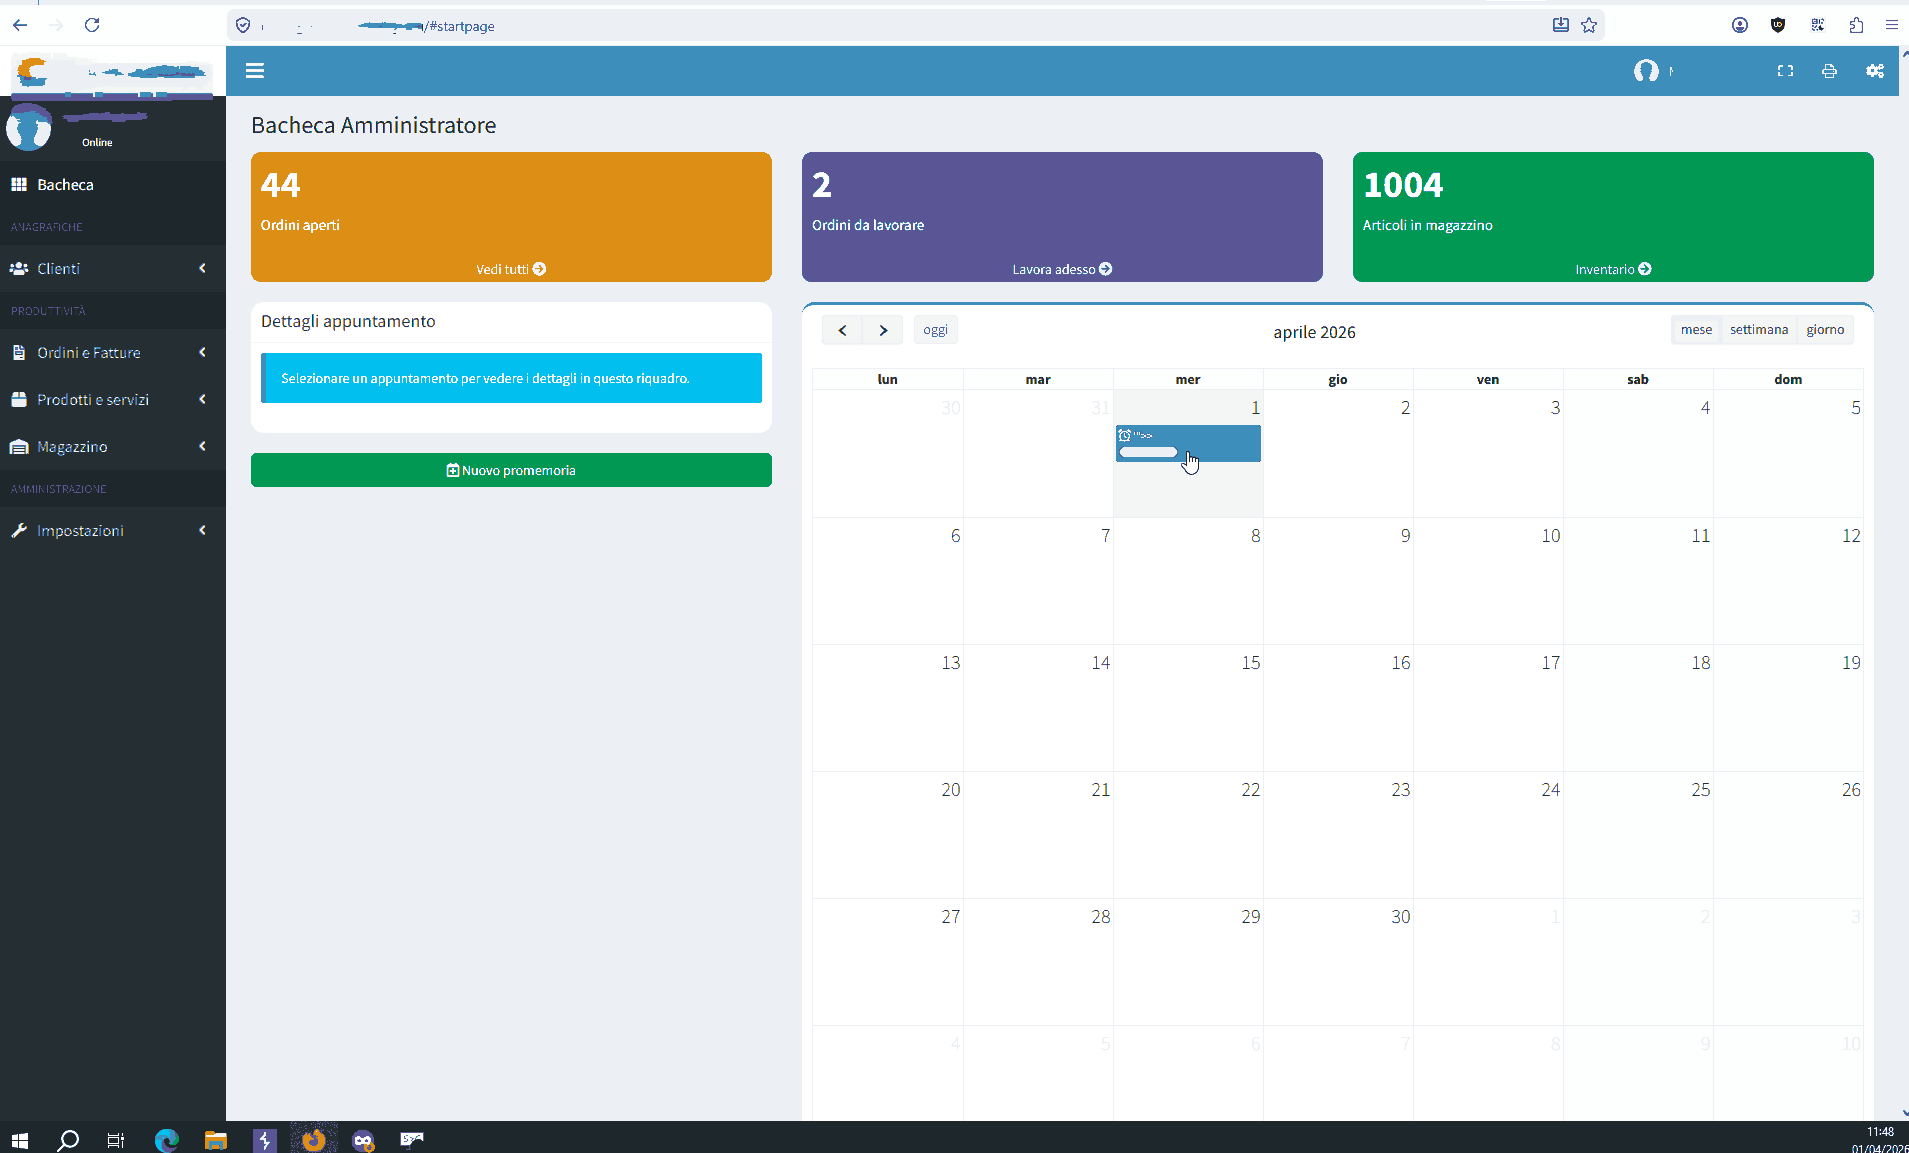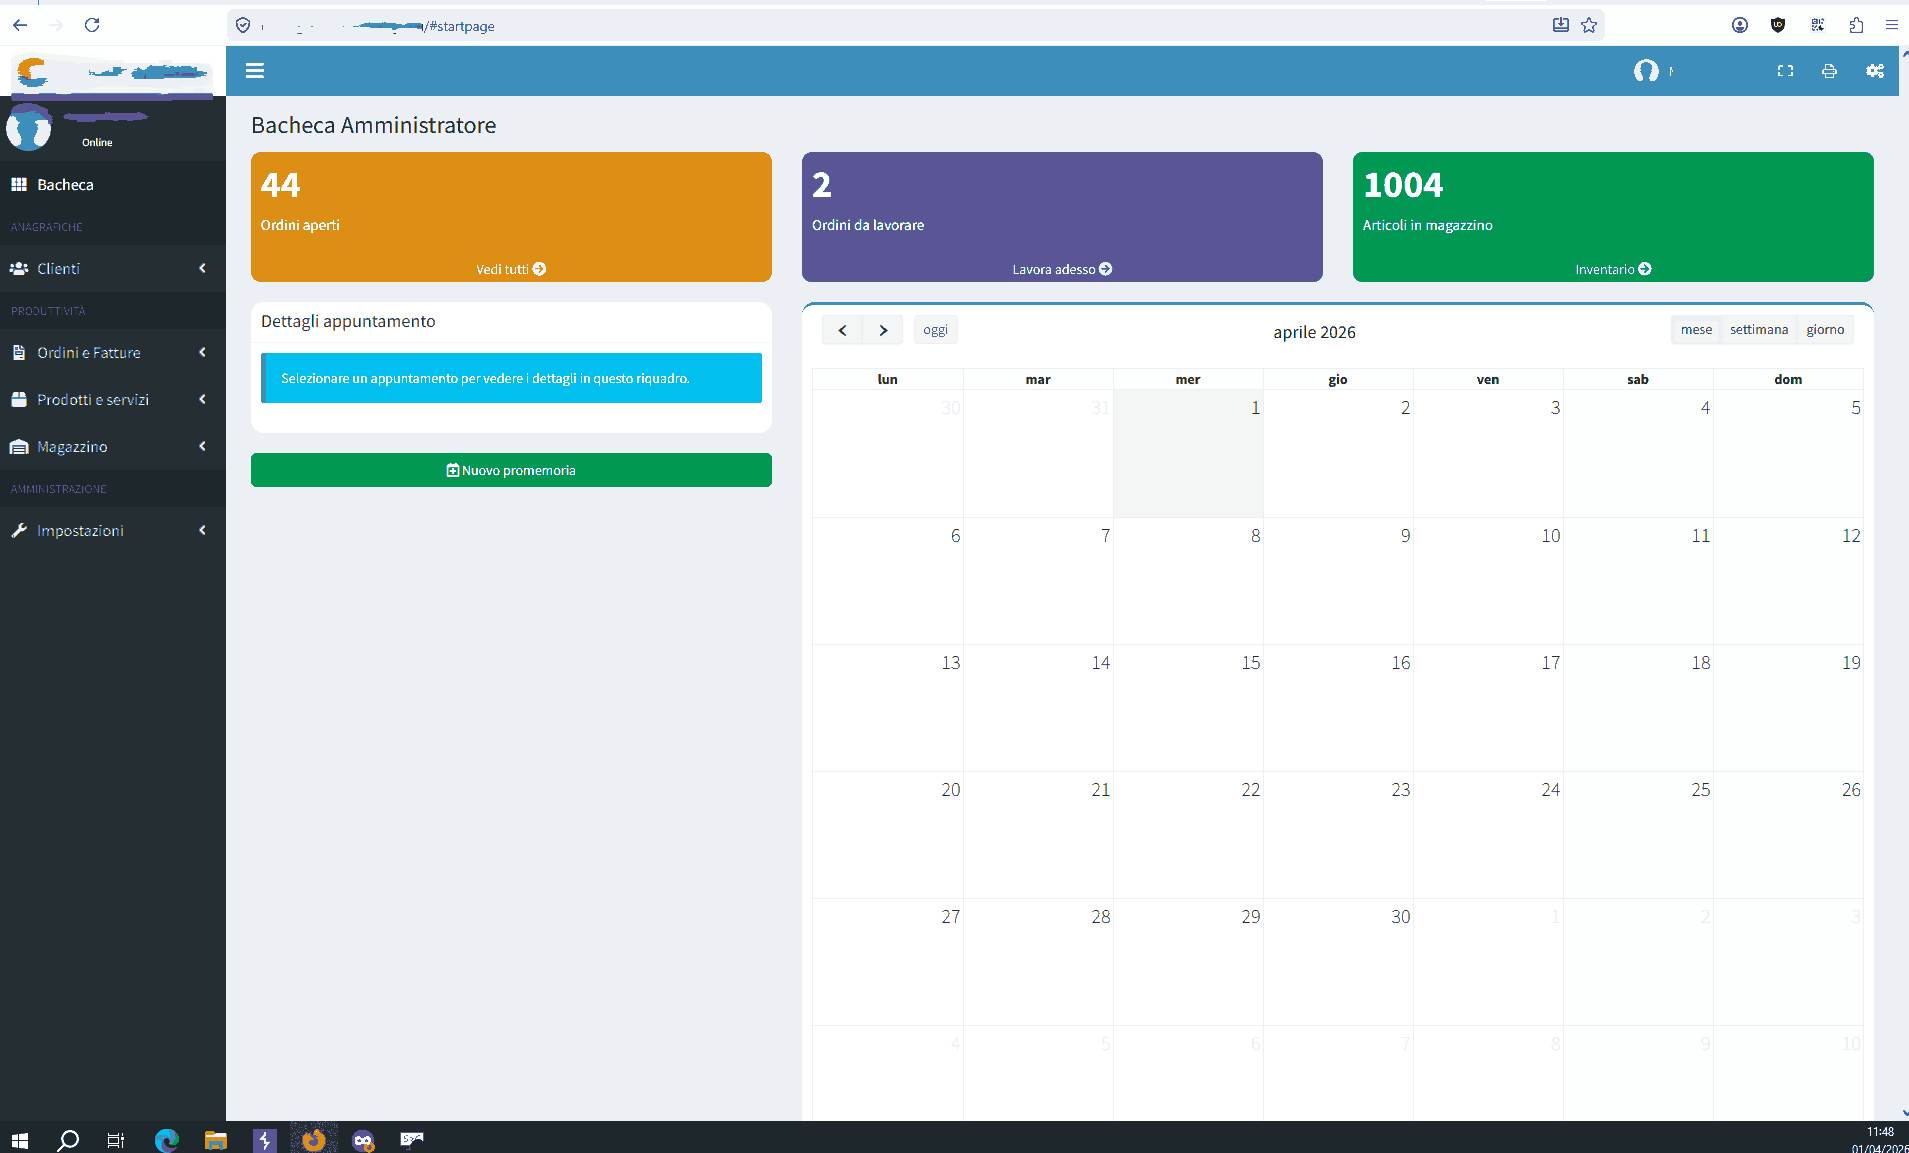
A vulnerability has been found in WebSystems WebTOTUM 2026. This impacts an unknown function of the component Calendar. The manipulation leads to cross site scripting. The attack may be initiated remotely. The exploit has been disclosed to the public and may be used. Upgrading the affected component is recommended. The vendor was contacted early, responded in a very professional manner and quickly released a fixed version of the affected product.
Weakness classification
- CWE-79: Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting')
- CWE-94: Improper Control of Generation of Code ('Code Injection')