VULNERABILITY INTELLIGENCE
CVE-2022-3118
CVSS score7.3 HIGH
EPSS probability0.86%
CISA KEVNot currently listed
Published2022-09-04
Last modified2026-06-17
CVSS vectorCVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:L/A:L
Description
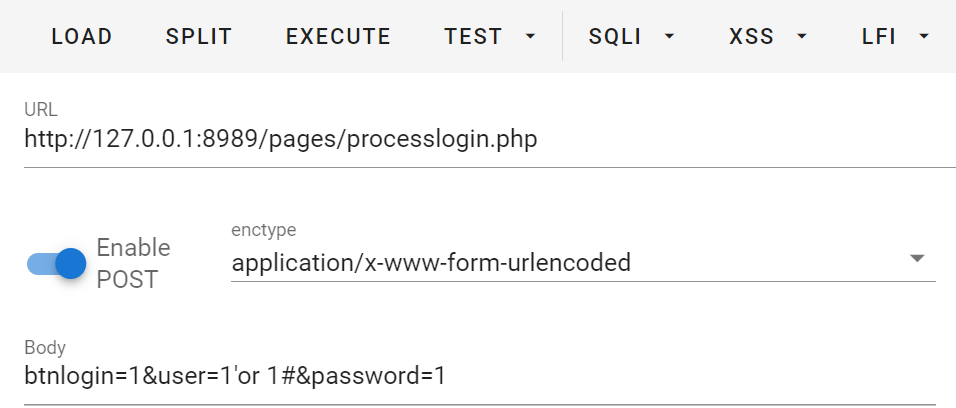
A vulnerability was found in Sourcecodehero ERP System Project. It has been rated as critical. This issue affects some unknown processing of the file /pages/processlogin.php. The manipulation of the argument user leads to sql injection. The attack may be initiated remotely. The exploit has been disclosed to the public and may be used. The identifier VDB-207845 was assigned to this vulnerability.
Weakness classification
- cna@vuldb.com: CWE-89
Primary references
- cna@vuldb.com — Exploit, Third Party Advisory
- cna@vuldb.com — Third Party Advisory
- af854a3a-2127-422b-91ae-364da2661108 — Exploit, Third Party Advisory
- af854a3a-2127-422b-91ae-364da2661108 — Third Party Advisory