VULNERABILITY INTELLIGENCE
CVE-2022-2909
CVSS score6.3 MEDIUM
EPSS probability0.85%
CISA KEVNot currently listed
Published2022-08-20
Last modified2026-06-17
CVSS vectorCVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:L
Description
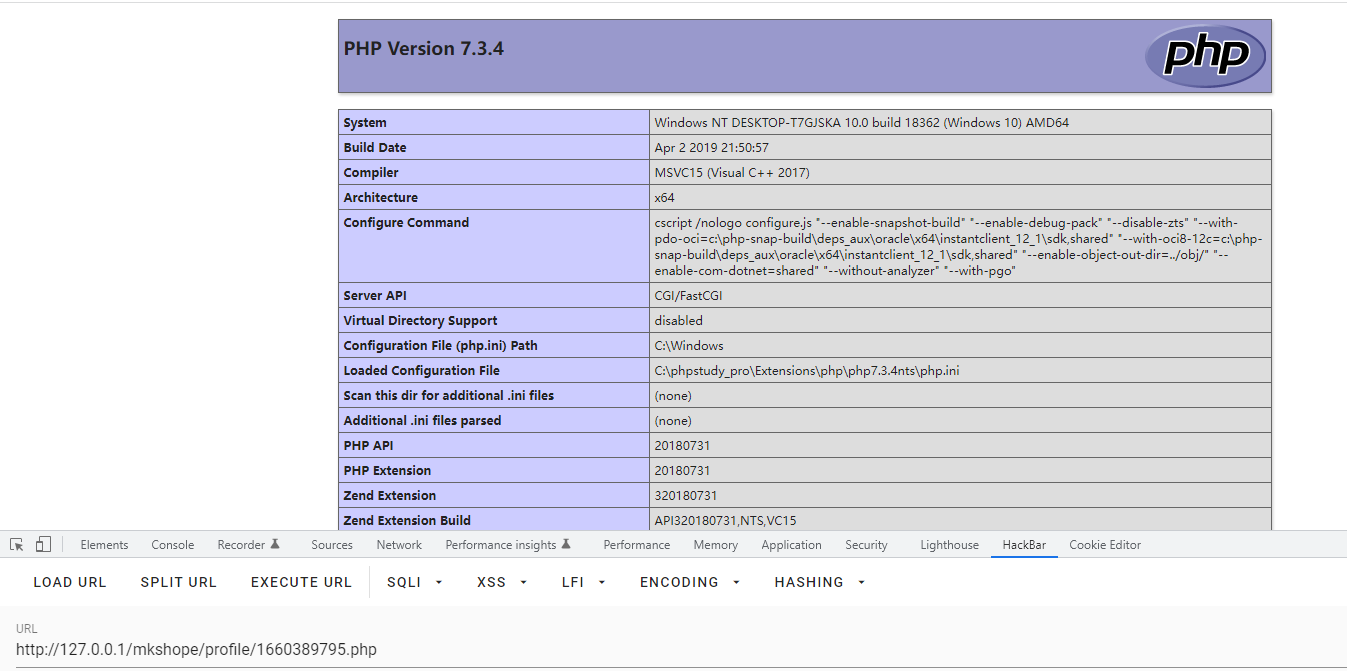
A vulnerability was found in SourceCodester Simple and Nice Shopping Cart Script. It has been declared as critical. Affected by this vulnerability is an unknown functionality of the file /mkshop/Men/profile.php. The manipulation leads to unrestricted upload. The attack can be launched remotely. The exploit has been disclosed to the public and may be used. The identifier VDB-206845 was assigned to this vulnerability.
Weakness classification
- CWE-434: Unrestricted Upload of File with Dangerous Type
Primary references
- cna@vuldb.com — Exploit, Third Party Advisory
- cna@vuldb.com — Permissions Required, Third Party Advisory
- af854a3a-2127-422b-91ae-364da2661108 — Exploit, Third Party Advisory
- af854a3a-2127-422b-91ae-364da2661108 — Permissions Required, Third Party Advisory