VULNERABILITY INTELLIGENCE
CVE-2022-2814
CVSS score3.5 LOW
EPSS probability0.63%
CISA KEVNot currently listed
Published2022-08-15
Last modified2026-06-17
CVSS vectorCVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:U/C:N/I:L/A:N
Description
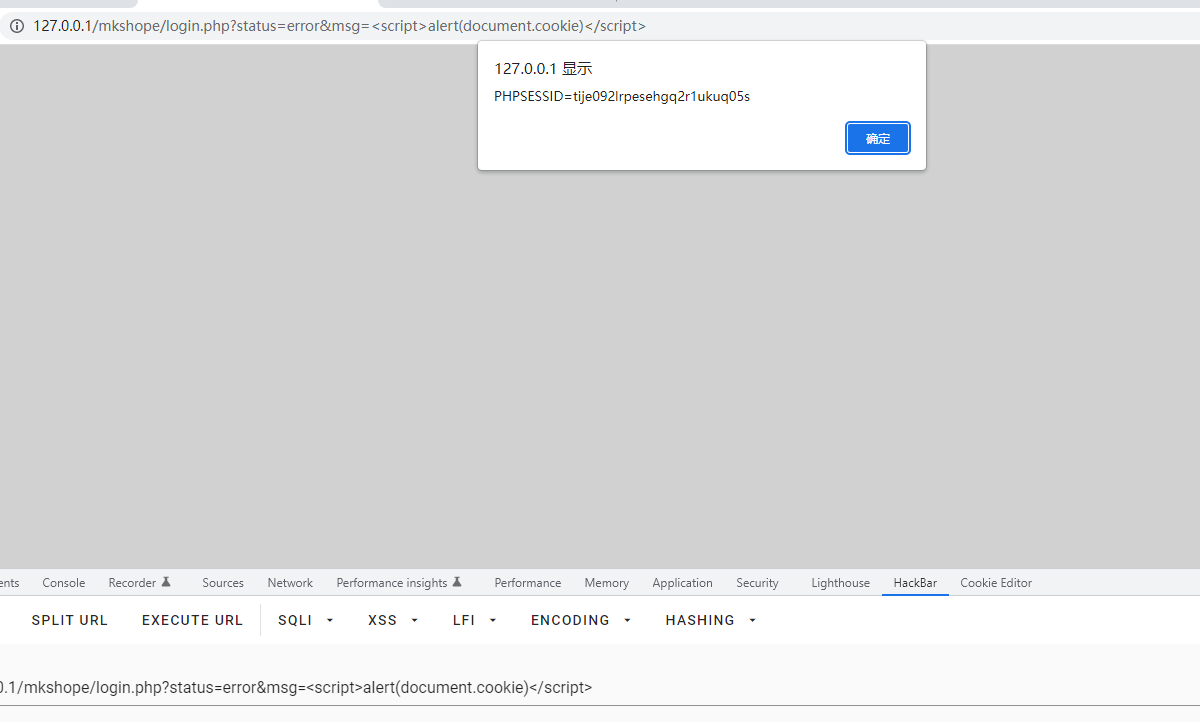
A vulnerability has been found in SourceCodester Simple and Nice Shopping Cart Script and classified as problematic. Affected by this vulnerability is an unknown functionality of the file /mkshope/login.php. The manipulation of the argument msg leads to cross site scripting. The attack can be launched remotely. The exploit has been disclosed to the public and may be used. The identifier VDB-206401 was assigned to this vulnerability.
Weakness classification
- cna@vuldb.com: CWE-79
Primary references
- cna@vuldb.com — Exploit, Third Party Advisory
- cna@vuldb.com — Exploit, Third Party Advisory, VDB Entry
- af854a3a-2127-422b-91ae-364da2661108 — Exploit, Third Party Advisory
- af854a3a-2127-422b-91ae-364da2661108 — Exploit, Third Party Advisory, VDB Entry