VULNERABILITY INTELLIGENCE
CVE-2018-19981
CVSS score7.2 HIGH
EPSS probability1.80%
CISA KEVNot currently listed
Published2019-04-04
Last modified2026-06-17
CVSS vectorCVSS:3.0/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H
Description
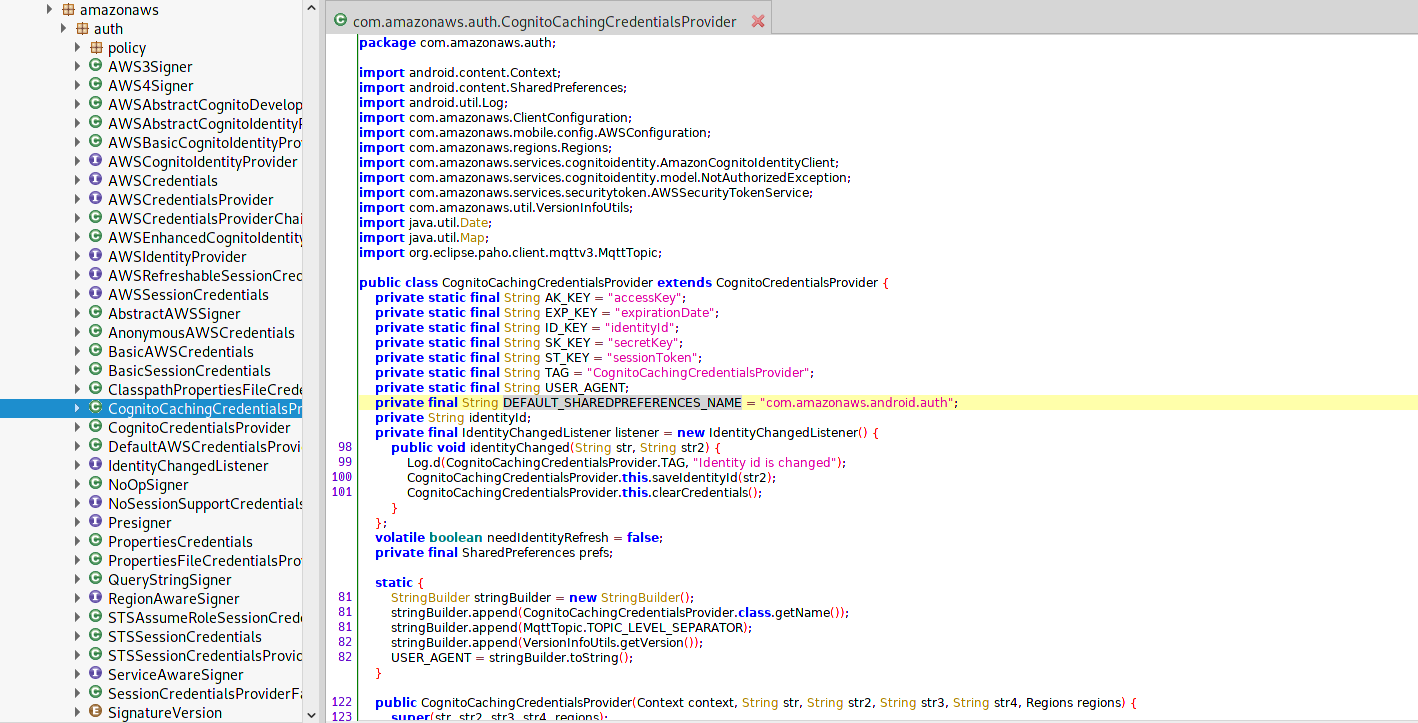
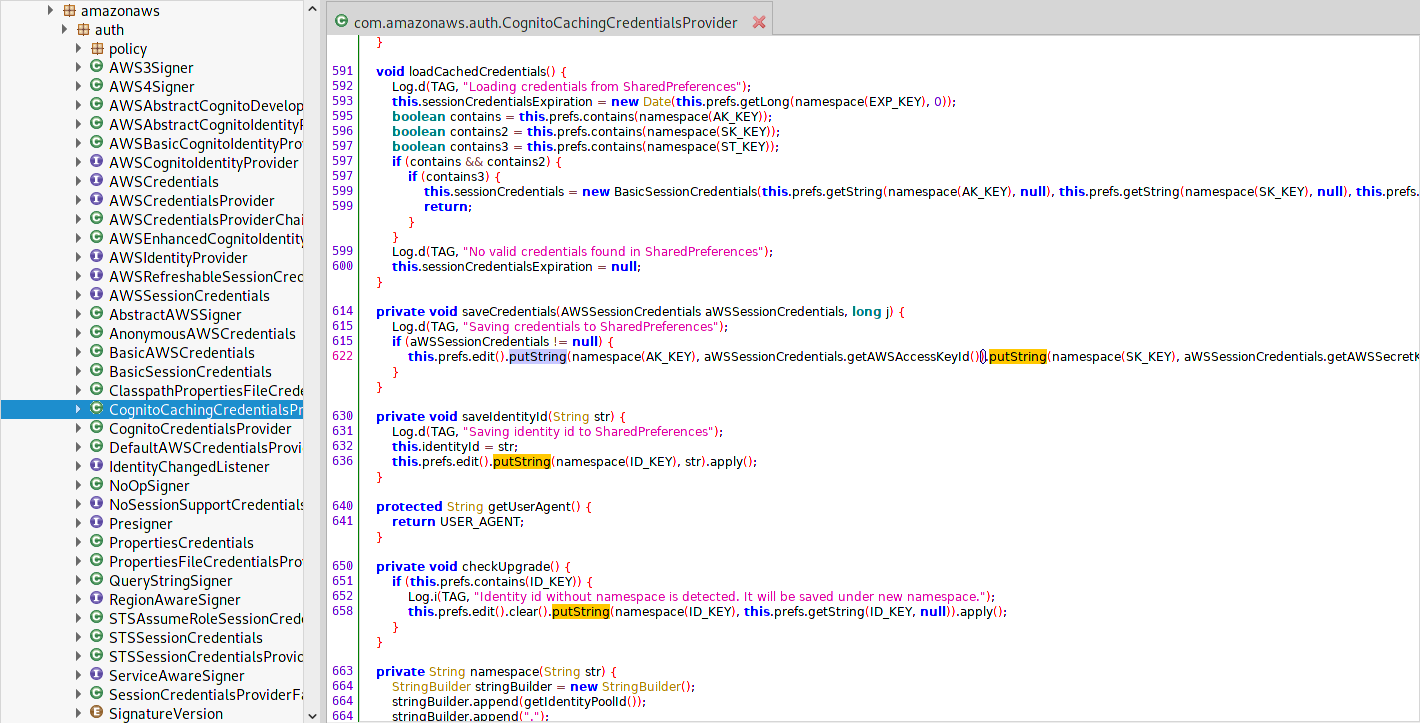
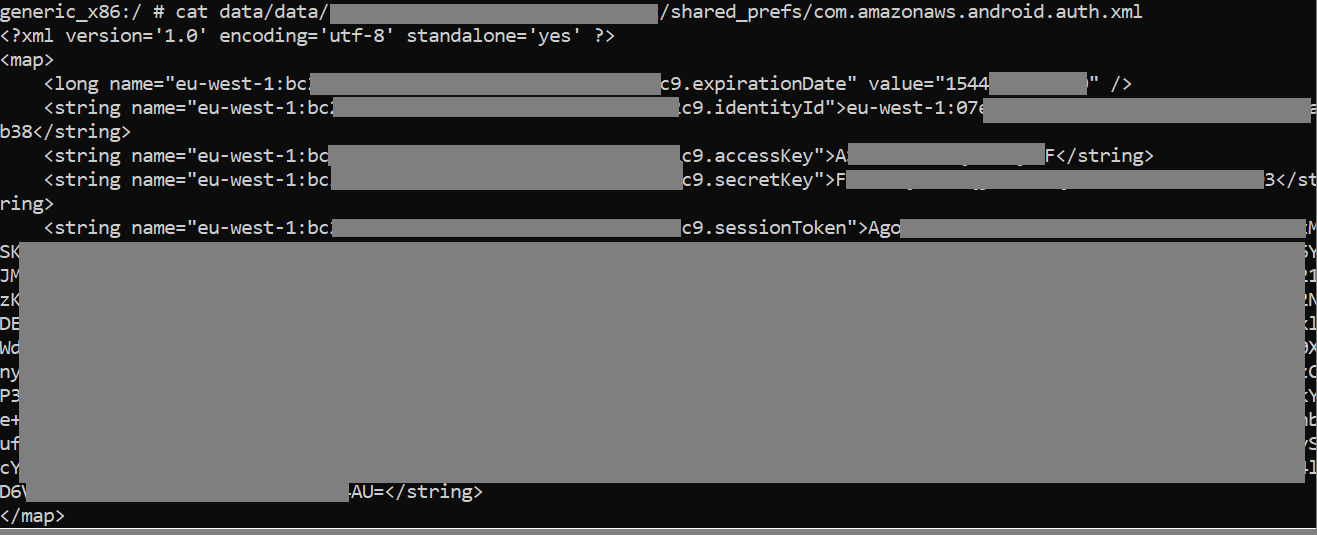
Amazon AWS SDK <=2.8.5 for Android uses Android SharedPreferences to store plain text AWS STS Temporary Credentials retrieved by AWS Cognito Identity Service. An attacker can use these credentials to create authenticated and/or authorized requests. Note that the attacker must have "root" privilege access to the Android filesystem in order to exploit this vulnerability (i.e. the device has been compromised, such as disabling or bypassing Android's fundamental security mechanisms).
Weakness classification
- CWE-312: Cleartext Storage of Sensitive Information
Primary references
- cve@mitre.org — Exploit, Third Party Advisory
- cve@mitre.org — Exploit, Third Party Advisory
- cve@mitre.org — Exploit, Third Party Advisory
- cve@mitre.org — Exploit, Third Party Advisory
- af854a3a-2127-422b-91ae-364da2661108 — Exploit, Third Party Advisory
- af854a3a-2127-422b-91ae-364da2661108 — Exploit, Third Party Advisory
- af854a3a-2127-422b-91ae-364da2661108 — Exploit, Third Party Advisory
- af854a3a-2127-422b-91ae-364da2661108 — Exploit, Third Party Advisory